❌

Lese-Ansicht

US data centers could wipe out 15 years' worth of progress in greenhouse gas emissions, report claims

Concerns have been mounting everywhere about the environmental impact of data centers, with alarms ringing at various environmental think tanks. The Sierra Club, one of the oldest environmental preservation organizations in the U.S., has now put forth an estimate that by 2030, U.S. data center buildouts will be outputting as much carbon dioxide as the entirety of Mexico, pushing back progress on greenhouse gas reduction by 15 years, Bloomberg reports.
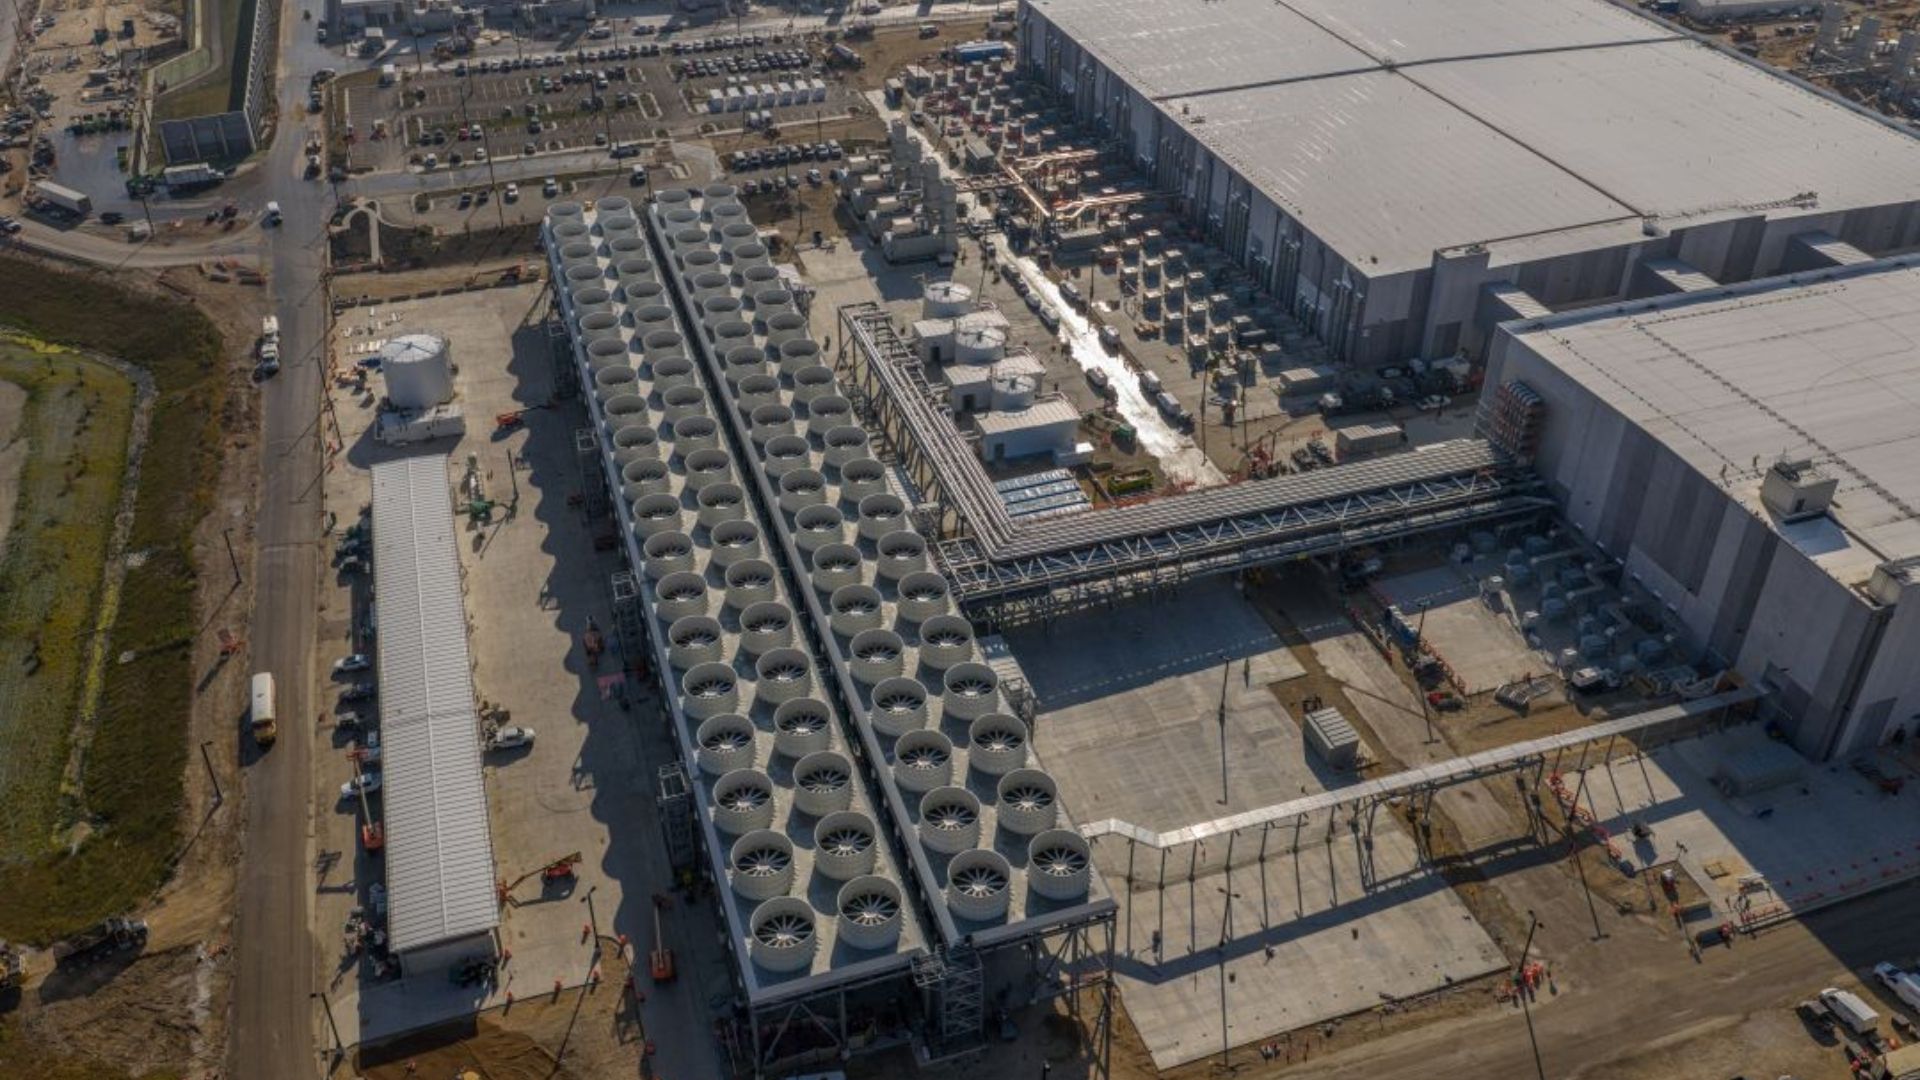
The Club's principal advisor for climate and energy, Jeremy Fusher, puts it plainly: "the numbers continue to sort of boggle our minds." He's referring to an estimate that with the output from pending data center builds, the output from the U.S. power sector is set to put 2.1 billion metric tons of CO2 in the atmosphere by the end of the decade, an uptick of 42% compared to 2025 figures. The researchers' previous estimates were between a quarter and half of the current projections.

An increasing number of countries and states are enacting laws demanding that new data center builds have a large portion of their power generated by green sources. However, those laws rarely apply retroactively, and oftentimes have a phase-in period. Even the Irish law on the matter demanding that new data centers be fed by 80% of renewable power only requires that that happens six years after they're powered up.

In the current AI-driven market, speed of construction is king. Roughly 40% of U.S. data centers are fed by natural gas turbines, and the situation doesn't look like it'll be changing much. It'll likely get worse, as the addition of green sources almost assuredly won't keep up with demand. Much like RAM, GPUs, and storage, turbines were all slurped up by data centers. Their prices have risen by 50%, and production is backlogged for years, with one maker stating it's opening slots for production in 2032.

Having said all that, Brendan Pierpont from Energy Innovation, another climate-concerned organization, points out that although the current path looks dangerous for the environment, it's hard to make a hard prediction of how the situation will play out. He justifies his position with common data center roadblocks: the availability of turbines, delays in grid connections, and other delay factors.

Truth be told, at this point it's hard to predict how many data centers will actually reach completion, given that requests for permits far exceed available grid capacity across the U.S., and a sizable number of buildouts are encountering strong opposition. Plus, although the AI bubble is still alive and well, concerns started to arise about the economics of hyperscalers, indicating some may go the way of the dodo — and their projects along with them.
  •  

Tech whiz's internet-accessible Synology NAS gets bit by ransomware attack from 18-month-old remote code execution flaw

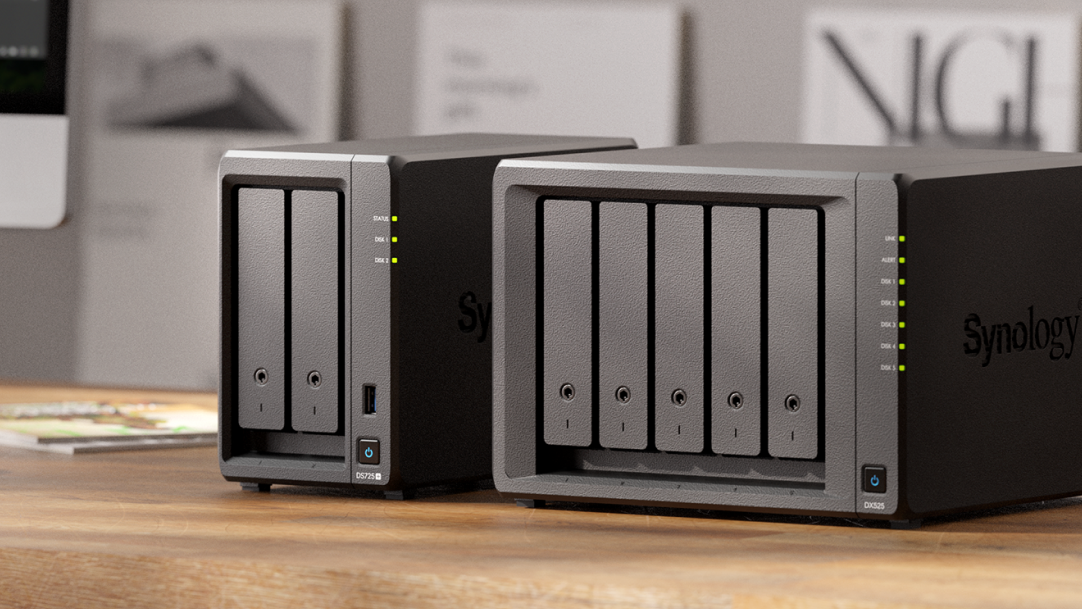
Systems administrators are among the first to point out lax security policies in other companies' or people's setups. Sometimes, they are the ones who get bitten by not taking the same advice they will so readily dispense. Such is the tale of Reddit user NakamuraHwang, who had files on their Synology DS918+ NAS encrypted by a ransomware attack after making a series of unforced errors.

Hwang appears to be quite technically proficient and provided a detailed write-up of the situation. The key points, however, are that the unit in question (a) had its web interface exposed to the internet and (b) was roughly 18 months out-of-date with security patches. Just like the recent PHP snafu has adeptly shown, complacency is a far worse enemy than an army of AI bots.

The tech has a 3-2-1 backup setup, so they seemingly didn't lose any data. They attached the disks to a Proxmox machine for further inspection — Synology's DSM operating system uses mdraid underneath, so you can take the disks to another box and mount them there. Investigation of logs and the operating system files revealed that the attack was likely performed by abusing the CVE-2024-10441 remote code execution vulnerability, revealed a year and a half ago.

As most any other sysadmin will tell you, it's never advisable to expose devices directly to the internet without some layer of protection in between, chiefly but not only a VPN or an SSH tunnel. Tailscale, for instance, makes having a VPN fairly painless these days, and its free plan covers most home installations.

Synology had published its own advisory regarding the exploit, but that's where the NAS' behavior regarding updates complicates matters. According to multiple comments on the thread and in other forums, the UI will happily tell you that your device is up to date, all while there are critical security updates that need to be manually installed. The manual for DSM indicates that units from 2025 onwards have automatic updates, apparently implying that those of previous makes need to be configured so.

Furthermore, Synology apparently doesn't have a direct channel to warn its customers of critical security vulnerabilities —a simple e-mail notification would suffice. Although the firm is seemingly shifting away from consumer gear, it still sells small units that regular users might buy, and it's not reasonable to expect them to even be aware of security bulletins. Plus, package updates like the patch for the PHP2Shell vulnerability have to be installed separately, too.

  •  

GitHub says massive influx of AI-generated code required extra 4 million CPU cores and 160 petabytes of storage to manage

Is most programming code now made by AI? That's not hard to believe given the number of testimonies, but we now have exact figures behind that statement. GitHub, the world's largest code repository, says that over the course of this year, it added 4 million CPU cores, 160PB of storage, and 50 Tb/s of networking capacity to keep up with the influx of AI-generated code.

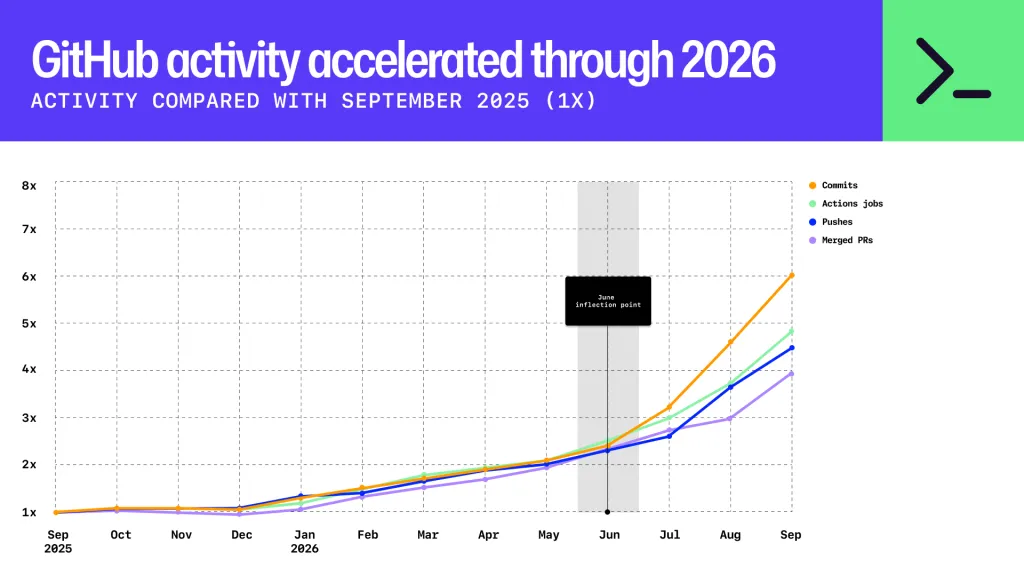
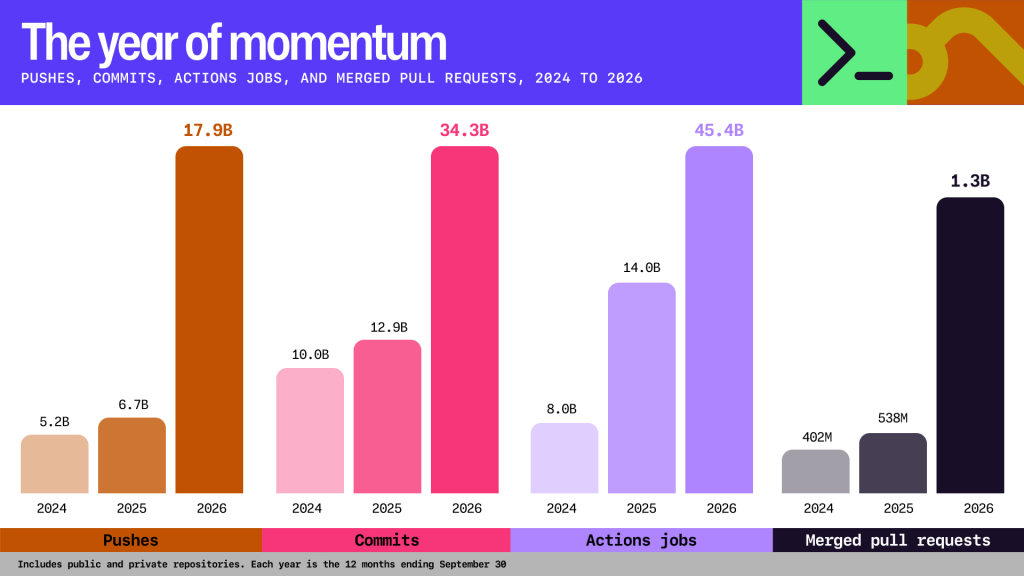
Raw repository activity saw a massive year-over-year increase, as per GitHub's technical report. Code commits (adding/removing code) grew sixfold, while merged pull requests (finalizing a feature or bugfix) jumped 4x.

The multipliers sound impressive enough, but the exponential growth pattern is even more so: half a year ago in April, there were already 1.4 billion commits per month — a figure that rose to 2.9 billion in August, and now sits at 7.4 billion for September. GitHub saw 17.9 billion code pushes in the past 12 months, which is more than all of 2024 and 2025 put together.

GitHub 2026 activity graph

GitHub 2026 activity graph (Image credit: GitHub)

Predictably, the company says that agentic AI is behind the dizzying rise in the amount of code, and the need for it to both upgrade and rethink its technological infrastructure. By last September, over 40% of pull requests were started by an agent, up from 17% in March 2026. Moreover, repositories that kick off using AI generally see eight times the activity compared to handcrafted operations.

All this code activity puts disproportionate strain on CI/CD pipelines. In modern development, whenever someone commits code or merges a pending pull request, many actions are triggered: for example, checking for leftover "to-do" items, visually arranging code for consistency (linting), and running code and integration tests to check that the new code doesn't break existing functionality within the application and works correctly with associated programs, services, and APIs.

GitHub activity progress

GitHub activity progress (Image credit: GitHub)

Triggering all of the above for each commit and/or pull request means that GitHub's hardware requirements have ballooned, now requiring massive amounts of computing power and I/O. The rise was so intense that the firm even had to reengineer its backend to try to decouple storage from compute as much as possible. Given how quickly demand is rising, GitHub is likely to have to upgrade sooner rather than later.

  •  

Why native PC ports of console games are suddenly everywhere

Over the past weeks and months, it's increasingly commonplace to encounter native PC ports of previously console-exclusive video games, developed with the help of frontier AI models and a new tool named Reverse Engineer Anything (REA). With dozens of titles ported to PC over the past few months, the big questions are: why is this now possible, and what changed?

The better-known conversions like Super Mario Galaxy and Modern Warfare 2 use AI agents, but their handlers mostly still had to interpret results and direct each step of the process. That's now much easier with Reverse Engineer Anything. Although it shows up in many conversations, REA doesn't do the heavy lifting by itself. It's actually a mix between a toolkit and agent harness, wiring together previously disparate tools under one ceiling.

REA analyzes and manages collected information tools: binary analyzers, decompilers, metadata tools, firmware images, database readers, and so on end up linked via agents. Those tools are made available to your AI agent of choice, along with skill files with additional instructions.

Simplistic as it may sound, it's the glue that once again significantly cuts down the time spent on "chores" that a developer would otherwise have to do while reverse-engineering code, which started with emulating consoles themselves.

Emulation of video game consoles on PC is nothing new, having emerged in the 90s in the 2D era, and gradually transitioning to 3D consoles such as the PlayStation 1, and Nintendo 64. Throughout the early 2020s, emulators and toolkits evolved at a rapid pace, covering more systems than ever — even the PlayStation 3 and its notorious Cell processor. Physical hardware is taken apart and inspected more easily and at deeper levels than ever, as tools like the Raspberry Pi become cheaper and more powerful. These elements set the stage for the ultimate task: to fully decompile and recompile a game and convert it to run on native PC instructions, rather than relying on software emulation. Only one barrier remained: dedicated development time.

To reverse-engineer a game, you need dozens of different tools, analyze the game's executable, run it, inspect which files it reads, which calls it makes to the operating system, what memory it allocates, and so on and so forth. This is exceedingly tedious, and yet can't be done half-heartedly: one errant byte is a bug. It's like undoing a machine with a million cogs and keeping track exactly where each one was, its size, and orientation. Modern games grew, too, and can have millions of lines of code.

But that kind of nitpicky, repetitive work is just what computers excel at — even non-deterministic ones like LLMs. 2026's AI models like GPT-6 Astra and Claude 5.5 families are "smarter" in the sense that they follow complicated instructions more closely and can better keep track of their tasks, granting them a higher degree of autonomy. The high token efficiency of lower-grade variants like Claude Sonnet also makes them somewhat affordable, if not cheap, to use on a humongous project like taking apart an entire game.

Given how AI bots can hallucinate and make up strange replies and code, you may wonder how a project of this scale ever gets accomplished. It's simple: your agent hands you decompiled source code, and it compiles it again to see if it matches the original byte-for-byte. Even if they hallucinate, the bots can try over and over until they get it right, and developers can correct them if needed.

Reverse-engineering needs multiple tools, all with their own technical terms and idiosyncrasies. Whereas before developers had to wrangle them across terminal windows, now you can get your agent to twiddle bits and talk between programs on your behalf, so long as you issue the right orders. They don't have to stop for breaks, either.

With relatively simple prompts, you can poke around and break down a game or application — provided you have one of the pricier agent subscriptions, or can absorb high token bills, as for example the Modern Warfare 2 decomp took three months and up to 700 billion tokens to accomplish. Had its developer used REA, he may have cut down on time and tokens both.

  •  

$4,700 audiophile-grade network hub promises a noise-free experience and music with 'emotional impact'

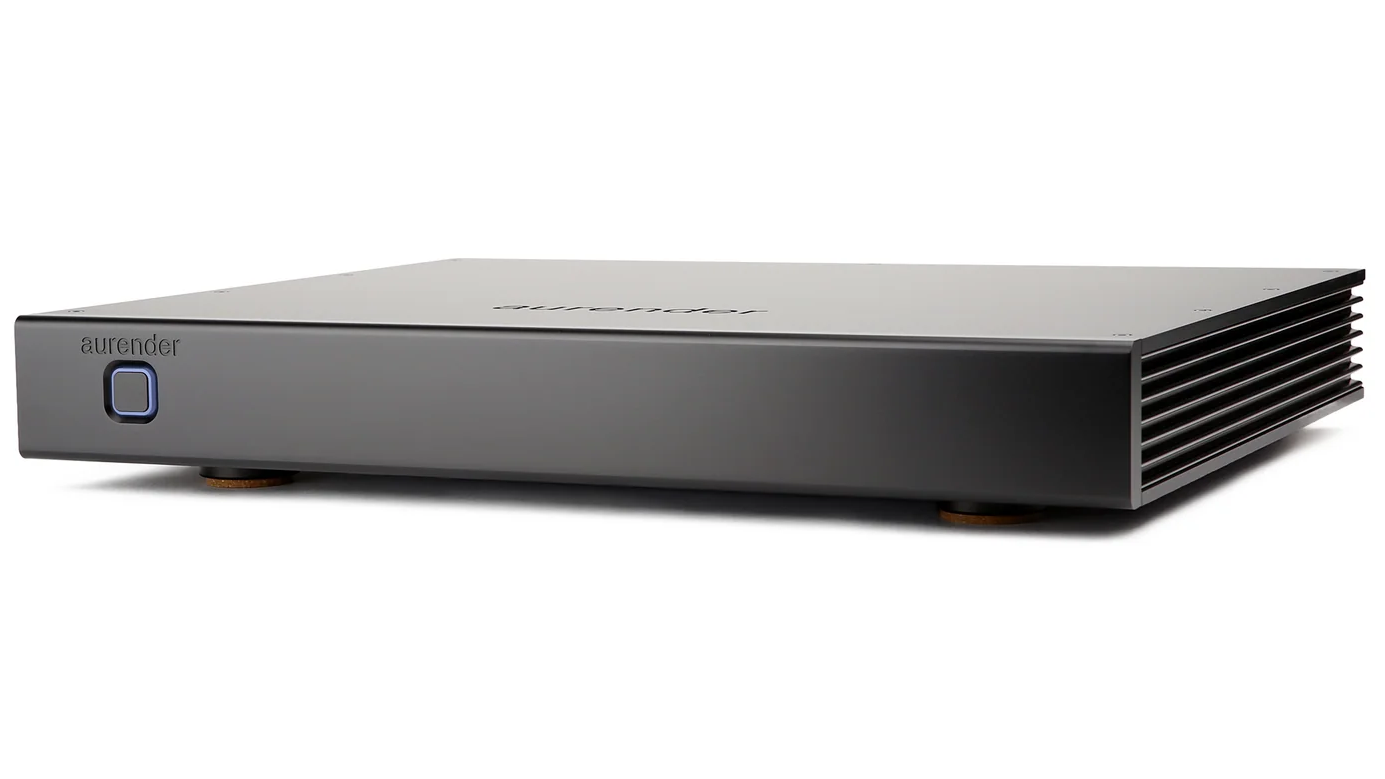
There are a lot of salesman sayings, and, chances are, most were inspired by audiophiles. The eternal sufferers of audiophilia nervosa keep coming up with novel ways to attribute sonic and emotional characteristics to any piece of equipment — even when discussing things purely in the digital realm. One of the current fads is audiophile-grade network switches, like the Aurender NH10 Network Hub, coming in at a mere $4,700.

This piece of gear —which we presume is actually a network switch, rather than a hub — comes fitted with eight gigabit ports. Six of those are standard copper inputs, while the other two are SFP ports where audiophiles can plug in a transceiver for either fiber or copper. The product page remarks that, naturally, a fiber connection is electrically isolated. I was teeing up a joke about the existence of audiophile-grade SFP transceivers when, while proofreading, I found that life does truly imitate art. Oh, and that $4,700 doesn't even get you 10 GbE capabilities.

Four of the six copper ports on the Aurender switch have a total of seven electrical filtering stages behind them, while the remaining pair "only" has two. According to an article at Headphonesty, Aurender's designer said the team experimented with using over 10 stages, but eventually settled on seven "from listening comparisons." That's an interesting feature considering that the Ethernet standard already mandates electrical isolation for standard twisted-pair connections.

Aurender also says that it's using an OXCO (Oven-Controlled Crystal Oscillator) controlled by an FPGA for clock synchronization, and there's a BNC input on the back for an external source. From what we can tell from the board picture, the main chips include: a Realtek RT8370N switch controller ($5.5 at LCSC, an MV85 oscillator ($39 on eBay), and an AMD/Xilinx Spartan 6 FGPA ($8-15 depending on model). There are, no doubt, more manufacturing and materials costs to go from a collection of chips to an assembled switch, but presumably not enough to get anywhere close to the $4,700 asking price of the NH10.

This is all adorable, but the fact of the matter is that the hardware here cannot, by any reasonable definition, make any difference to the sound. TCP connections have built-in error correction. The Ethernet protocol includes Cyclic Redundancy Check (CRC), and there are several similar layers, up to the point where the data turns into an actual analog signal.

It's also up to whichever equipment is handling the playback to electrically isolate the actual DAC output stage, not at the network or switch level. And even affordable audio interfaces have signal-to-noise ratios that 1970s recording engineers would happily give up their LSD for.

Likewise, the whole conversation about jitter is pointless, though much like any audiophile myth, it's grounded in a piece of truth — just one that's completely irrelevant in this scenario. In a recording studio, you occasionally need to sync the clock across multiple pieces of gear, just like matching tape machines back in the day. For just the one piece of playback gear, however, it's pointless, and it's downright nonsensical at the network level.

Yet logic has never stopped some self-described audiophiles. One can but wonder what folks seriously looking at these pieces of gear would feel knowing that the studios where their precious music is being made use, for example, one bog-standard Ethernet cable to carry 4 balanced analog lines. Or how their favorite guitarist's pedals and amplifier in a famous recording session were held together with lamp cord, duct tape, hopes, and dreams.

  •  

Data center gear is being hijacked in transit to the tune of hundreds of millions

Have you been watching many heist movies lately? Here's a Hollywood-ready script for a new one: Organized crime teams have taken to stealing data center gear off or with their transport trucks, to the tune of tens of millions per shipment. They employ hacking and phishing, vehicular ramming, GPS signal spoofing, and have ties to international crime networks. An extensive report on NBC sheds light on this new trend, remarking that over $100 million dollars of computing and related gear were stolen via transit interception in various guises since June 2026 alone.

This type of heist has been growing over the past couple of years, but just this year the one incident in Reno made $38 million in gear disappear. In the same city, $15m of semiconductors and Apple products got nabbed in July 2025, according to Fortune. The month of June 2026 was particularly profitable for thieves, as they made off with $13m of gear around the Mojave Desert area, and $10m worth of server rack components headed to Texas.

The stolen gear includes servers, fiber-optic and copper cabling, RAM modules, drives, routers, and other miscellaneous gear. Although NBC doesn't mention GPUs by name, stolen data center servers headed for AI buildouts are likely to have some.

Even copper wire is worth a lot these days, as one snagged trailer had $300,000 worth of the now-precious metal. As Keith Lewis from Verisk Cargonet puts it, "it's like stealing pure gold bars [...] it's so much easier to steal [data center shipments] than to rob a bank."

The methods used employ technological smarts and brutality in equal amounts. Each heist is unique, but broad patterns are apparent. Thieves gain access to online accounts of freight brokers and carriers, and from there on they can look up cargo manifests and shipping schedules, as well as impersonate shipping companies. Then they track a shipment or issue a false one, and eventually collect the truck with the precious cargo.

In a few recent cases, the heists involved thieves literally ramming escort cars so that the truck executes a trouble-free getaway. In those cases, the truck driver was likely in on the play, and probably got in the driver's seat thanks to the prevalence of AI-generated IDs coupled with poor personnel vetting practices.

And as for GPS trailer tracking, the malfeasants thought of that too: in one case, they seemingly used GPS beacon impersonation and broadcast fake coordinates so that neither human nor automated system believed anything was amiss.

The first instinct is to assume that all of the gear would end up on the second-hand market. But in an additional twist to the story, the thieves already have overseas buyers ready before the heist actually takes place.

Law enforcement officials believe that the gear is slurped up by entities operating in countries under the U.S.' tight AI export controls, including China. Verified Carrier, a platform for vetting carriers, says that this year, it's seen suspicious activity linked with U.S. cargo theft in India, Uzbekistan, Pakistan, Colombia, and Moldova. Scott Cornell of TAPA Americas estimates that six to seven out of 10 stolen cargo shipments (data center gear or otherwise) end up overseas.

David Warrick, of supply management firm Overhaul, describes the scale of the problem: "These are international syndicates. They run like big corporations…They have penetrated the supply chains at all levels, in terms of drivers, in terms of warehouse operators. They know where all the high-value goods are; they know who transacts them, and they look for the weak points in the supply chain to be able to exploit those."

  •  

Intel quietly confirms Raptor Lake Next CPUs through internal driver publication

Intel has published an internal test driver with the "RPL-NEXT" label, presumably in reference to Raptor Lake Next CPUs that Tom's Hardware first reported on in June. On the same day as the driver was uncovered, shipping manifests from Vietnam were published by Club386, showing exports of CPUs labeled "Raptor Lake Next" dating back to August, complete with cache and clock speed information.

➡️ https://t.co/jatYVFZ9egOctober 26, 2026

The driver was first spotted by @momomo_us on X, and we were able to find it by searching the name in Intel's software database. The file is locked (hence the padlock icon), and clicking on it will redirect you to an Intel login page. Given that and the "testbuild" label, it looks like this is an internal driver test that wasn't meant to be published.

Judging by the existing conventions, the driver package is for the Smart Sound Technology (SST), a audio digital signal processor integrated into the silicon since the Alder Lake days. Audio codecs like those of Realtek use SST for offloading duties like noise reduction, echo cancellation, low-power audio playback, and wake-on-voice without adding to the CPU load, and saving precious watts in the process.

For broader context, Raptor Lake Next is Intel's refresh of the Raptor family of CPUs, meant to plug into existing LGA-1700 motherboards. Given the currently insane DDR5 memory prices, gamers ought to be happy on two fronts: getting newer chips for their existing motherboards, and the ability to use more affordable DDR4 instead, an ability all but confirmed by Gigabyte's recent BIOS updates.

According to Club386's shipping manifests, there are so far four chip models en route from Intel's Vietnam facilities. Their specs suggest that they're replacements for extant Core i5 and Core i7 models, as a previous leak indicates that Intel doesn't yet have any plans for replacements for its Core i9-14900K chip.

As such, the listed models should top out with the 99DLMV part number, with 16 cores in an 8P + 8E arrangement, a meaty 3.5 GHz base block, and 30 MB of cache (presumably L3). This is the only model with a 125W TDP, and its base clock is higher than that of the Core i9-14900K, so it should be a speedy enough affair despite not having the high core counts of the halo models. Chances are it'll be a nice gaming CPU with pretty high turbo clocks, but only reviews will confirm that.

Interestingly, the 99DLMT has 20 cores (8P + 12E), but its much lower 65W TDP and 2.1 GHz base clock, which indicate that this model might be an efficiency-oriented productivity chip. In the table below, we added our guesses as to which models match existing chips.

Part number

Cores / Threads

TDP

Base clock

Cache

Approximate matches

99DLMV

8P + 8E (24)

125 W

3.5 GHz

30 MB

i7-14700 / i7-13700

99DLMT

8P + 12E (28)

65 W

2.1 GHz

33 MB

i5-14600K / 13700K

99DLMW

6P + 4E (16)

65 W

2.6 GHz

24 MB

i5-14400 / i5-13500

99DLMX

n/a

65 W

2.6 GHz

24 MB

As above

There's no word about pricing, but we'd expect the new chips to ring in at roughly the prices of the existing models. As points of reference, the Core i7-14700 is currently $366, or $330 for the "F" variant without integrated graphics. At the lower end of the above table, the Core i5-14400 is sitting at $208, or only $161 without an IGP.

  •  

Lack of staff and funding likely led to the recent PHP security snafu; project has only one full-time employee, but that's just the tip of the iceberg

The AI-powered inrush of software vulnerability reports over the last year has shined a light on how many critical pieces of open-source software are chronically underfunded. The latest victim is PHP, the scripting language powering about 71% of websites, making the news due to a critical remote code execution vulnerability. The PHP Foundation, which develops and oversees the language, reportedly counts only one full-time person and 14 "mostly part-time" contractors. That's bad enough, but the real problem goes far deeper thanks to the internet's lazy development practices and systems administration.

In an interview with Reuters, the PHP Foundation's Executive Director Elizabeth Barron spells it out clearly: she's the only full-time person on staff, and works with the contractors' help. Pertaining to the software itself, the team's job is to develop and maintain the PHP core, including taking care of security fixes. The core team accepts contributions from the world at large, in an arrangement not too dissimilar to Linux kernel development — except that project is far better-manned, with many full-time contributors and company-employed developers.

Naturally, the PHP foundation collaborates with other companies and many cybersecurity firms, but the dev team was stretched thin even before the increase in security vulnerabilities with the help of countless AI agents. Barron does note that there was no reported exploitation of PHP2Shell before the security fix came out.

But the lack of a higher funding level likely led to the "structural failure" to address the underlying vulnerability in a timely manner, as the out-of-memory condition (OOM) that eventually led to the 2026 exploits was originally discovered in 2024. Given how widespread PHP is, and how many third-party extensions there are, the work on fixing the OOM problem "stalled and restarted repeatedly over months." It didn't help that the Chainguard security firm broke the PHP2Shell embargo too early by accident.

Even still, the team is thankful for the money it has, as "without the Foundation’s funding it would have been impossible to have multiple people work on this issue full time, eventually through weekends and around the clock to coordinate and communicate with other involved parties." One would hope that this latest incident releases the purse strings of more companies that make their living off of PHP.

And yet, this failing is far larger than just bugs in the core language, which, notably, were only one point update away. In theory, any server running the current 8.x brand of the software should be upgraded in minutes with the released patches, but reality was far different, as websites went down for hours or days out of fear of exploitation.

The real problem reared its ugly head: nearly 73% of PHP installations were running versions well past their end-of-life (EOL) date, meaning that obtaining fixes is now far harder. Many professionals who worked with the language, including yours truly, had spent decades warning of this reckoning, even considering many Linux distributions were backporting fixes.

Many of these servers were still running PHP 7, a version that was completely EOL'd four years ago, with many years of advance warning, and that originally came out in late 2015, almost eleven years back. If that doesn't sound silly enough, let it sink in that around 7.7% of PHP sites were still running version 5.x, which first saw the light of day 22 years ago in 2005, and saw the final sunset in 2018. It's safe to say that everyone had plenty of time to prepare.

To further illustrate the ridiculousness of collective complacency: the jump from PHP 5 to 7 and then from 7 to 8 required changing sections of website code, but the vast majority of said changes are simple to find and apply, and even before AI, there were already automated code-patching tools around. A couple years ago I mapped them all out for a PHP 5-to-8 codebase conversion myself.

Most of the alterations were about dropping support for ancient functions and libraries, which themselves had had long-standing warnings of incoming deprecation. Not a lot of core language features underwent modification, and a lot of convenient syntax was added to help clarify fiddly, error-prone code, too. That the overall situation got to this point beggars belief and illustrates how complacency, laziness, and cost-cutting are a far bigger force than a cadre of AI bots digging for flaws.

  •  

YouTuber escapes the modern AI tech market by recreating his 1996 PC

These days, it's exceedingly difficult not to be jaded and weary about the tech market. Memory, graphics cards, and now storage are becoming impossible to obtain; there's basically no new consumer hardware being released; and there's AI everywhere. Technology YouTuber TrashBench (TB), too, is tired and was harkening back to the halcyon days when everything was fresh and straightforward — so he went back in time with a retro build.

More specifically, he recreated a facsimile of the first machine his parents bought him in 1996 when he was a wee lad, to play The Need for Speed: Special Edition — a PC-improved version of the first ever game in the series. According to the man, it was thanks to this machine that he fell in love with computers in general.

TB kicked things off with an Intel Pentium MMX 200 MHz CPU sitting atop an Epox Pronix EP-P55-BT motherboard, boasting what was at the time a new, fresh, convenient ZIF (Zero Insertion Force) socket. This motherboard popped up during the RAM transition from SIMM to DIMM, which is why you'll see two slots of each on the top. 32 MB of RAM went right in, a generous amount for the year.

Funnily enough, the CPU barely needed cooling, which is why a simple 40-mm fan suffices, although anyone who's lived through this era will tell you that those were guaranteed to start whining after just a few months of heavy usage. There is no case cooling, as it's just not needed.

However, he did need to correctly set the motherboard's jumpers, as such luxuries like automatically detecting CPU speed and voltage were just becoming normal. Yes, this meant that you could burn out a CPU if you played the jumper game wrong.

For graphics card duty, he enlisted an S3 Trio32 card, which was pretty, ahem, modest even in the era, and had no 3D rendering capabilities whatsoever. In this era, the now-ubiquitous 3D accelerator cards were just coming into fashion, and he eventually replaced the S3 with a Matrox Mystique 3D, another offering of dubious quality. Yet those were happy days, as any form of 3D acceleration was far better than none.

Storage comes by way of a Western Digital Caviar 22100 hard drive with a whopping two gigabytes of storage and the uncanny ability to emulate the dulcet tones of a jackhammer. TB eventually swapped it later for a roomier 80 GB unit. Again, due to the idiosyncrasies and constant transitions of the era — hardware doubled in speed and capacity nearly every year — he had to set a jumper to clip it to the likely amounts of either 8.4 GB or 33.4 GB, as the addressing space of BIOSes and disk controllers of the time were limited.

The build wraps up with an OG Sound Blaster 16 sound card and a CD-ROM drive. After test-driving the machine with Need for Speed, he moved on to Microsoft Flight Simulator 98, which necessitated a joystick. Naturally, he got the much-beloved Quickshot QS-123, a staple in many home PCs, and one that needed replacement in about six months, as its build quality matched its price.

  •  

Deepseek's latest AI model is smarter than ever, but its low running costs come at a price

Deepseek just upgraded its V4.1 Flash open-weight model to revision 1017. What looks like a mere point revision may actually be a significant step forward in model efficiency. On the product page, Deepseek uses the slogan "wish-driven programming made real," a likely reference to the colloquial "vibe coding," implying the model is a good fit for open-ended tasks with broad descriptions. However, while the model is indeed cheap and scores well, it can be hallucination-prone.

LLMs are roughly divided into two categories: closed commercial efforts from frontier labs, whose models are expensive to run but deliver excellent results, and Chinese open-weight competitors that broadly exchange reliability for a much cheaper running cost, particularly for long-running agentic tasks.

Deepseek V4.1 Flash (DSF) is a Mixture-of-Experts (MoE) model with 552B total parameters, 16B of which are active during runs. The model is multimodal, accepts both text and images as inputs, and its context window length measures the now-standard 1 million tokens.

According to Deepseek's internal benchmarks, the model slots in neatly between GPT-5.6 Sol and Claude Opus 5, even beating Anthropic's LLM in task tests. That's already a strong showing, but this latest revision of DSF shines in the performance-per-task base and token efficiency. The upgrade from V4 Flash to V4.1 Flash significantly slashed hardware requirements, with V4.1 using only one-quarter of the HBM and one-eighth of SSD storage for its KV cache compared to its predecessor, spending only 890 bytes per token entry.

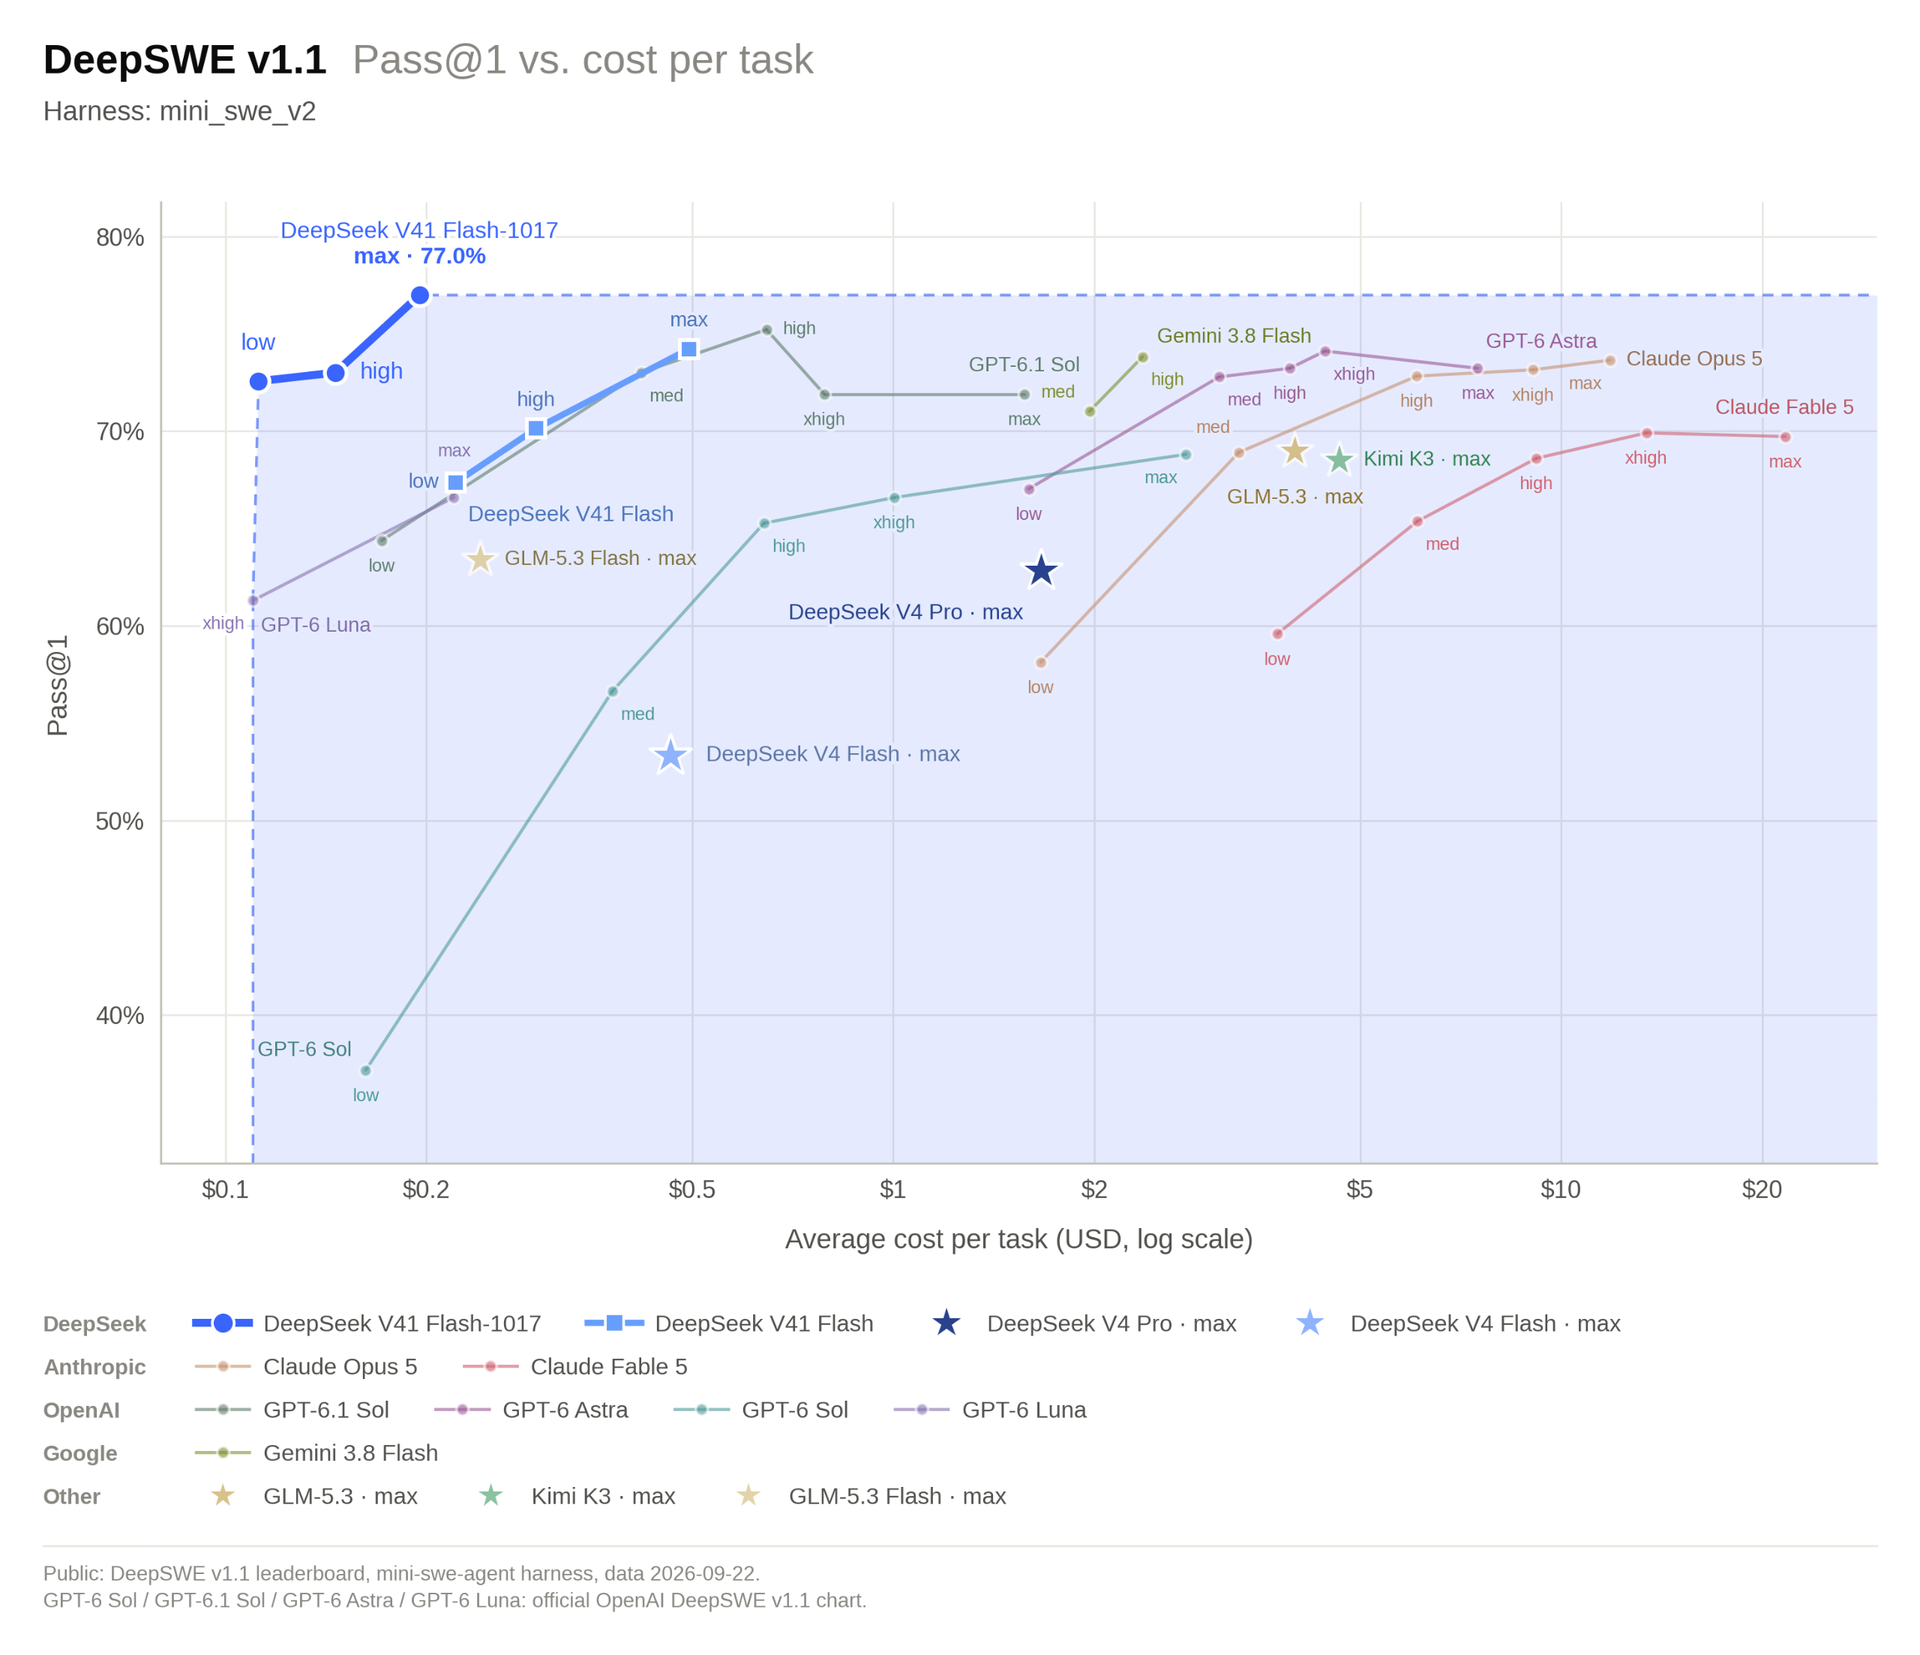
The company illustrates the point with a cost-per-task graph based on DeepSWE's dataset from September 2, adding its own data points for both DSF and DSF-1017. Both variants cluster in the desirable top-left area, and even low-effort runs of DSF-1017 offer a task completion rate in the ballpark of "max" settings for pricey competitors. It's worth noting that DeepSWE is only one of many benchmarks, but this is nonetheless an impressive result.

DeepSWE - Deepseek V4.1 Flash - 1017

(Image credit: Deepseek)

Even at Deepseek's own pricing (remember, this is an open-weight model you can run anywhere), the price at off-peak times per million tokens is just $0.15 for input and $0.6 for output. On cache hits, the input token cost drops to a mere $0.003. It's worth keeping in mind that third-party providers have undercut Deepseek API in the past, so those figures could go lower if you shop around inference providers. Deepseek also offers search functionality at $0.75 per 1,000 queries, an amount that undercuts competitors, with the closest one being Parallel at $1.

DeepSWE isn't the only benchmark around, either. Artificial Analysis ranks DSF-1017 (max) as only #2 on its intelligence index within the large open-weight class, with a score of 45. For reference, the most seemingly intelligent model, Claude Opus 5.5 (max with fallback), rings in at 58. It's one of the fastest models in its category, too, and its cost-per-task is edged out only by Xiaomi's MiMo V2.6-Pro.

This all sounds too good to be true, but everyone knows the adage of "fast, cheap, and reliable, pick two." So what's the catch? In one word: hallucination. Just because a model is smart doesn't mean it's reliable. Broadly speaking, users prefer models that don't answer when they lack supporting facts, and DSF-1017 doesn't seem very good at knowing what it doesn't know.

Artificial Analysis' Omniscience benchmark is quite clear on this matter, ranking the model among the lowest. It answered questions correctly 43% of the time, which is among the best for open-weight models, but inferior to the proprietary competition. That would be perfectly acceptable if it skipped answers without a foundation, but it hallucinated 67% of non-answers.

The benchmark's main index grants points for good answers and deducts them for wrong ones, and non-answers don't count. DSF-1017 gets 5 points, compared to Kimi K3-max's 20, with the frontier models coming in at 42+. Ultimately, this means DFS-1017 is by no means incompetent — much the opposite —but one should be careful about which tasks to assign to the model.

Tasks with verifiable outputs like programming, OCR with review, and format conversions will be fine, as the agent can run verification steps against its work and try again. However, open-ended research, looking up facts, and interpreting or drafting highly precise documents are tasks better suited to a frontier model — or, you know, a human — as hallucinations likely won't be properly reined in and results won't be very trustworthy.

"Fast and loose" seems to be a forming trend for highly competent open-weight models, too. Several months ago, when Kimi K3 was released, everyone raved about how effective and cheap it was, and how it proposed to offer frontier-level intelligence for a fraction of the price. My personal experience with Kimi was short-lived, as even short but precise fact look-ups came up with hallucinated information, and Artificial Analysis' data seems to back this observation up.

Nevertheless, open-weight models remain important both to make AI agents more accessible in absolute dollar terms and potentially as a tool to drive down the cost of intelligence when facing down potential price rises from frontier labs.

  •  

Leaked private keys for eight CA certificates let any attacker impersonate any domain

Most everyone in the tech space has been living in interesting times, but this week isn't done yet, and it's already quite special for systems administrators worldwide. They already had to deal with the critical PHP RCE vulnerability, but they also have to update untold amounts of machines and software, thanks to eight insecure intermediate CA certificates that can allow attackers to impersonate any domain and/or pretend their malware is from a legitimate source.

An attacker anywhere in the path of your network traffic, like, say, in a company or government network, public Wi-Fi, your ISP, or one of any number of government entities, can intercept your connection and pretend that they're any website, like apple.com, amazon.com, or bankofamerica.com. If not updated, your operating system and installed software would be none the wiser. Additionally, with the code signing certificates, an application you download can be shown as completely legitimate from, say, Microsoft or Google.

The way that software checks a certificate is legitimate is by verifying its "chain." For example, a website like tomshardware.com has a certificate, issued and signed by an intermediate Certification Authority (or CA, a certificate-selling company), and whose certificate, in turn, is trusted and signed by root certificates — whose exceedingly precious keys are kept offline in safes. In this week's event, Indian CA firm eMudhra issued six TLS and two code-signing intermediate certificates with easily guessable keys.

Your operating system and potentially tens of different applications on your machine all keep a list of which root certificates and CAs are trusted. Browsers also keep a list of those not to trust, called a revocation list. These lists are updated periodically as screw-ups happen, just like the one that took place this week. And now they all need to be updated again, by revoking the eight CAs, removing the one affected root certificate, or just hard-coding a rejection of all eight affected keys.

There's a silver lining: recent versions of Chrome, Brave, Firefox, and Safari all enforce a feature called Certificate Transparency that consults a public read-only log of certificate issuances, and blocks any that aren't mentioned. Google reports that no certificates signed by the six affected intermediate CAs were logged, so if regular web browsing is all you did, you should be safe — but still check all your software for updates nonetheless.

The problem here is the sheer amount of machines and software that needs updating: PCs, servers, operating systems, phones, tablets, routers, web browsers, web browsers wrapped in apps, virtual servers, virtual machines, Docker and other containers, programming languages like Python, Go, Node.js, Rust, standalone download utilities like curl, and probably tens or hundreds of other categories. Additionally, we discussed things that are expected and likely to get updates. Old routers, smart and IoT appliances, and old computers could eventually present a problem.

As for the technical details, eMudhra issued six intermediate CA certificates and two intermediate code-signing certs with rather unadvisable private keys. The private key is the secret half of the two parts of a certificate, and for some reason, those of the aforementioned certs were only 1 byte long — thus a number from 0 to 255, trivial to brute-force in a split second. How the heck that happened is still under investigation.

  •  

AMD's FSR 4.1 now works on Radeon RX 6000 cards, Xbox Series X and S, and Ryzen AI Max, AI 9, and Z2 SoCs

Earlier this year, AMD brought the previously RX 9000-exclusive FSR 4 upscaling tech to Radeon RX 7000-series graphics cards and promised an early 2027 release for RX 6000-series products. Christmas has come early for RDNA 2 and many other Radeon gamers, as Radeon honcho Jack Huynh has announced an FSR 4.1 release for Radeon RX 6000-series cards, Xbox Series X and Series S consoles, Ryzen Z-series handhelds, and machines with Ryzen AI Max and AI 9 chips today.

To accomplish this feat, AMD says it tweaked FSR 4.1's neural network model to support the INT8 shader hardware (as opposed to the higher-precision FP8 matrix acceleration hardware on Radeon 9000 cards). Additionally, the version specific to handhelds is slimmed down even further, to less than half the size of the full one.

AMD says that compared to FSR 3, games on the aforementioned GPUs and APUs will now deliver better image quality, all else equal. With Cyberpunk 2077 running in FSR Balanced mode at 4K, our quick testing with a Radeon RX 6900 XT shows that running FSR 4 costs just about 13% performance, a small price to pay for sharper and more stable visuals, especially in motion.

And the higher upscaling quality of FSR 4.1 might let gamers use Performance mode where they might previously have used Balanced, or so on, which might offset that performance cost.

There are more goodies in store, too. The Radeon team says that FSR Frame Generation now ought to have better frame pacing, resolving a longstanding complaint with the tech and potentially making for smoother gameplay with framegen enabled. Support for the Vulkan API with FSR 4.1 is set to arrive at some point, as well, a boon for some games and console emulators. Finally, AMD says FSR Ray Regeneration will also be coming to more games, too. The company showed the tech running in Warhammer 40,000: Darktide, and that integration is available now.

To get all this goodness into your GPU, you can download the just-released Radeon 26.10.1 drivers from the AMD Adrenalin application or directly from AMD's website. The updated software also adds support for Call of Duty: Modern Warfare 4, Star Wars: Galactic Racer, and Final Fantasy Resonance. You can check out the full release notes here.

For owners of Xbox and Ryzen Z2-series handhelds, AMD says that an update from their manufacturers will be forthcoming, as those devices depend on OEM-specific drivers.

We're pleased to see that Radeon gamers are getting upgrades for their existing graphics chips along the lines of what Nvidia has been delivering throughout 2025, because the way things are going, it looks like it'll be around 2077 before there will be a new gaming graphics card launch. If you're an RDNA 2 gamer, go give FSR 4 a shot and see what you think.

  •  

US restarts three shut-down nuclear reactors to feed AI data centers

The current and expected power draw of AI data centers has been the subject of strong discussion, but today, there appears to be some good news. Three U.S. nuclear reactors are being restarted after many years offline, expected to bring 2.25 GW total to the grid. According to a report, the Palisades Nuclear Plant in Michigan, the Crane Clean Energy Center on Three Mile Island (Pennsylvania), and the Duane Arnold Energy Center in Iowa are getting a fresh set of proverbial tires to get rolling again.

The Palisades plant was under active decommissioning, apparently marking this event as the first time a nuclear reactor is being put back to work after dismantling had begun. Despite what sounds like a tough starting point, this plant is the one that's furthest along, as it was loading fuel in August 2026 and is expected to generate 800 MW around March 2027.

Much like the other projects mentioned here, the Holtec Palisades firm running the reactor took a loan from the U.S. Department of Energy. Palisades borrowed from the DoE under the Biden administration's 2024 investment in nuclear energy, while the others were issued under the purview of the Trump administration's 2025 push.

The second reactor is the Crane Clean Energy Center on Pennsylvania's Three Mile Island, repurposing the facility's Unit 1. The project started in 2024, with Constellation Energy saying it would spend $1.6 billion total for the reactor. The firm then took a $1 billion loan from the Department of Energy in 2025. Microsoft is set to be the main customer, with a 20-year contract. This facility is projected to bring 835 MW online sometime in 2027.

This facility was famous in 1979 for the partial meltdown of its Unit 2, although mercifully the event had relatively tame environmental consequences. Constellation's ongoing project is restoring and refurbishing Unit 1, which didn't show significant issues until its 2019 decommissioning and has undergone a safety inspection from the Nuclear Regulatory Commission. This entity still needs to grant its blessing before the reactor starts loading fuel.

The Duane Arnold Energy Center in Iowa is the third unit being brought back to the grid, in a collaboration between NextEra Energy and Google. The predicted output is 615 MW, with the juice expected to start flowing in 2029. Next Energy CEO John Ketchum stated that the firm was happy with its cooperation contract with Google, as it meant that "none of the costs are being paid by residential customers in Iowa."

All three facilities had previously been shut down at various points as they were deemed too expensive to run, as labor and maintenance costs made nuclear-generated watts pricier than alternative means of production.

But the financial landscape for power has shifted, plus with such overwhelming demand and grid connections being a primary blocker for data center buildouts, their operators are likely willing to pay for premium power as long as they get it now instead of in a few decades.

Some quick browsing indicates that Michigan is going to need somewhere between 1.2 and 2.3 GW for data centers alone around 2030. Pennsylvania's forecast has a wide range of 0.8 to 3.4 GW, while Iowa's range is 1.55 to 2.8 GW. These figures are loose, as they include planned capacity for data center projects that may or may not end up being built, and whose timetables may slip due to economic conditions, hardware availability, and public resistance against expansive buildouts.

  •  

Modern software is built on the backs of low-paid maintainers, opening the door to potential threats

Modern computing systems and devices typically require pieces of crucial open-source software, typically maintained by unpaid or low-paid volunteers. Recently, a report collated a list of critical open-source projects, noting which of them are chronically underfunded and/or understaffed. The information is sobering: 11 out of 23 of the listed projects currently only have one or two maintainers, and funding is generally scarce and sometimes nonexistent.

The Data Drop's report on open-source maintainers identifies that having only one or two sets of eyes on critical pieces of software means that sooner or later something breaks — and it tends to do so in spectacular fashion, given its ubiquity. So, what happens when these projects, which are widely used across software, go underfunded or understaffed?

Lessons from the past

In 2014, the same year as Heartbleed, Shellshock made waves: a vulnerability in the Bash shell that's present in Linux, macOS, and Unix-type systems. The problem was traced back to a line of code present since 1989, displaying how even software that's thought to have all the bugs hammered out of it can still fall prey to attacks. A quick look at Bash's commit history shows it's almost exclusively maintained by Chet Ramey.

In 2016, ImageMagick was exploited, providing attackers with remote code execution. This library is used for image manipulation across a wide range of software, in webpages, mobile apps, and more. A 2020 analysis revealed that hundreds of security issues had been found over the years in its extensive codebase. Nearly every code contribution in the past couple of years has been done by an individual named Dirk Lemstra.

Contemporary examples include 2021's Log4Shell exploit, a critical vulnerability in the Apache Log4j logging library used in millions of servers. The libwebp image-handling library saw a zero-day vulnerability in 2023, and the xz compression library used across Linux and iOS was compromised in 2024.

Thankless work

Key points in the report mention specific repos, which might be under threat. Somewhat unsurprisingly, the low number of overall maintainers and the unpaid nature of the work make it unattractive to perform.

The main time-zone file used across Linux-based operating systems is maintained pro bono by Paul Eggert, a UCLA teacher. Core-js, a piece of support software that lets new JavaScript work in old browsers and is estimated by the author to be used in half of the busiest websites in the world, is handled by Denis Pushkarev. He once had to endure criticism from the community because he added a command-line message to the library's installer asking for help or a job.

The HarfBuzz library developed by Behdad Esfahbod is a cornerstone in ligatures and text shaping in Middle Eastern languages. In those writings, a letter changes shape and/or orientation according to what's around it. Esfahbod handles that vast majority of the project's code, and doesn't mention public or corporate funding.

Libjpeg-turbo handles JPEG images on Android, Firefox, LibreOffice, and every Chromium-based browser. It's kept ship-shape by D.R. Commander aka DRC, who occasionally is contracted for library-specific work, though at arguably modest values of "3-4 figures rather than 6 or 7." Libxml2, just like the label says, handles XML reading and writing across numerous applications and operating systems. Nick Wellnhofer, the original maintainer, stepped down in September 2025, after years of work with little income.

The SQLite project provides a one-file database that's exceedingly easy to integrate into most software, instead of complicated, resource-heavy databases, while still retaining standard SQL language and accouterments. Thanks to its ease of use, it found its way into an astonishing number of applications. Examples include WhatsApp, Dropbox, Android, Windows, and all major browsers.

The project estimates that there are about a trillion instances of SQLite in use. Just four people keep this critical project together, and they've gone to the length of removing their names and photos from the project's page, as "there are a lot of crazy people in the world who might misuse that information." The project is funded by the offering paid support via the founder's company, though there's no word on effective income, especially when it presumably needs to feed four mouths.

Funding is there, but scarce

It's not all doom and gloom, though. Take curl (the software), for example. Almost every developer has used it, thanks to its URL-fetching abilities and extensive scripting options. The project was started by Daniel Stenberg, who is now paid to work full-time on it. The team has now grown to 11 and has received funding through Open Collective and Germany's Sovereign Tech Agency, among others.

Likely due to the lessons learned from their past respective debacles, both the Log4j and OpenSSL projects are likewise funded by the Sovereign Tech Agency, as are the FFmpeg video file handler and the OpenSSH secure shell software that's ubiquitous in Linux servers.

All things considered, it's easy to argue that the critical importance of all the aforementioned software merits sizable investments from industry players, especially those whose commercial products benefit the most from the community's efforts. Plus, even if the firms feel no moral obligation to contribute, in the day and age where AI agents are finding exploitable vulnerabilities in hours, donations to these open-source projects could also be considered investments.

  •  

Typo-squatting attacks with major domains are still viable

When the IETF decided to allow Unicode characters in domain names, many techies saw the move as commendable, but also fraught with danger, as hundreds of unique characters can look similar or identical across multiple alphabets. This can be used for typosquatting attacks, wherein bad actors create functioning websites with deliberately misspelled web addresses that look identical to the real URL, thus launching attacks against unsuspecting visitors who land on the site due to search results generated when the user mistypes an address. The Chromium browser has the most advanced ruleset for finding and preventing mischievous domains masquerading as legitimate ones, but even the best code has odd edge cases, as a blog post from Have I Been Squatted (HIBS) explains in great detail.

Using "аррӏө.com" as an example — which is in fact not identical to the real "apple.com" — the researchers show how specific combinations of characters can still evade multiple layers of protection, thanks to the particular circumstances surrounding the use of specific Cyrillic characters. This alphabet has lookalikes for many Latin letters. For example, а → a, е → e, о → o, р → p, and с → c. We forgive you if you can't spot the differences.

Trying to sneak the one homoglyph into the middle of standard Latin ones triggers Chromium's safeguards and makes the browser display the domain name in its Punycode format. For example, using the Cyrillic "а" with "pple.com" would show up as "xn--pple-43d.com". With few exceptions, domain names with non-Latin characters ending in .com only pass the check if they're all from the same alphabet.

Having said that, opting to try "аррӏе.com," using all Cyrillic lookalikes, would also go bust. Chromium keeps a list of 29 Cyrillic characters that routinely masquerade as their Latin counterparts, and composing a domain name using only characters from that list is a no-no.

So how does "аррӏө.com" pass? Allow us to illustrate with bigger text below. Note how the right-hand Cyrillic character is actually an oval with a line across it.

[e] ≠ [ө]

As you can surmise by now, the "ө" character is not in that special list of 29. While a more recent release of Chromium can and probably will add it, this reveals the difficulty of the problem: since there's no one-size-fits-all solution for detecting typo-squatting, even the best set of rules will sooner or later end up on the wrong side of a corner case.

It takes many watchful eyes to play Unicode Pokémon and catch'em' all, especially given the character set continually evolves and now counts nearly 173,000 entries — though only a subset of those are eligible to be used as domain names or TLDs in practice.

Chromium is reportedly the best browser at detecting domain lookalikes, as a 2020 study showed that it caught 64.1% of the attempts, with Firefox and Safari trailing behind. As a reminder, Chromium underpins the Chrome, Edge, and Brave browsers.

Besides many other rules and per-alphabet verifications, Chromium keeps a list of over 8,000 popular domains bound to be typo-squatted, and runs stronger checks against 836 of them. Domain registries, likewise, make reasonable efforts to prevent typo-squatting, like having strict rules about what characters can go into which TLDs, but that's not nearly enough to fully solve the problem.

All things considered, HIBS recommends that companies afraid of impersonation try to register any lookalike domains and try to encourage passkey use by users. Passkeys are always tied to a specific domain, so a user wouldn't be able to log in to a sneaky website with them.

  •  

Grab an RTX 5090 for a discounted $5,300 as part of an MSI Infinite ZS prebuilt gaming PC

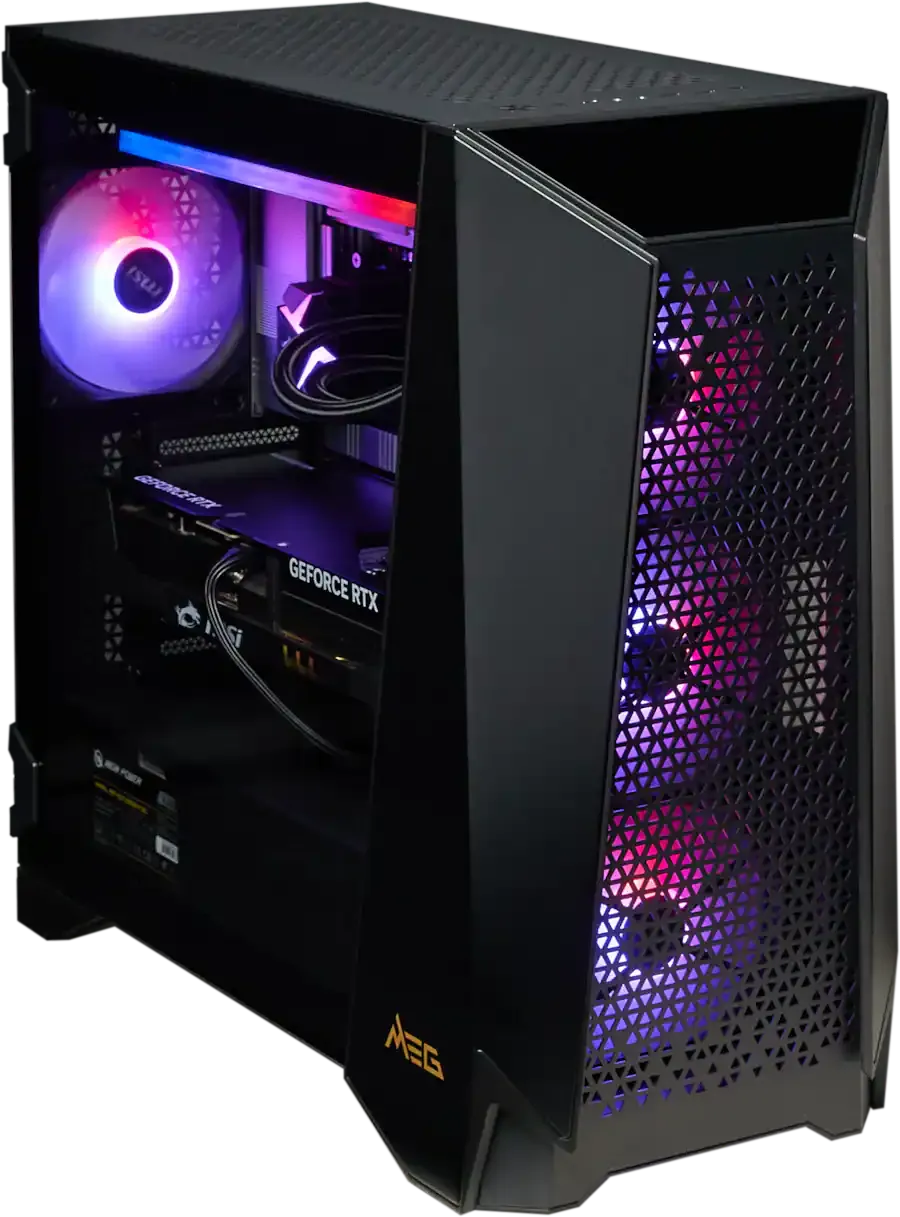
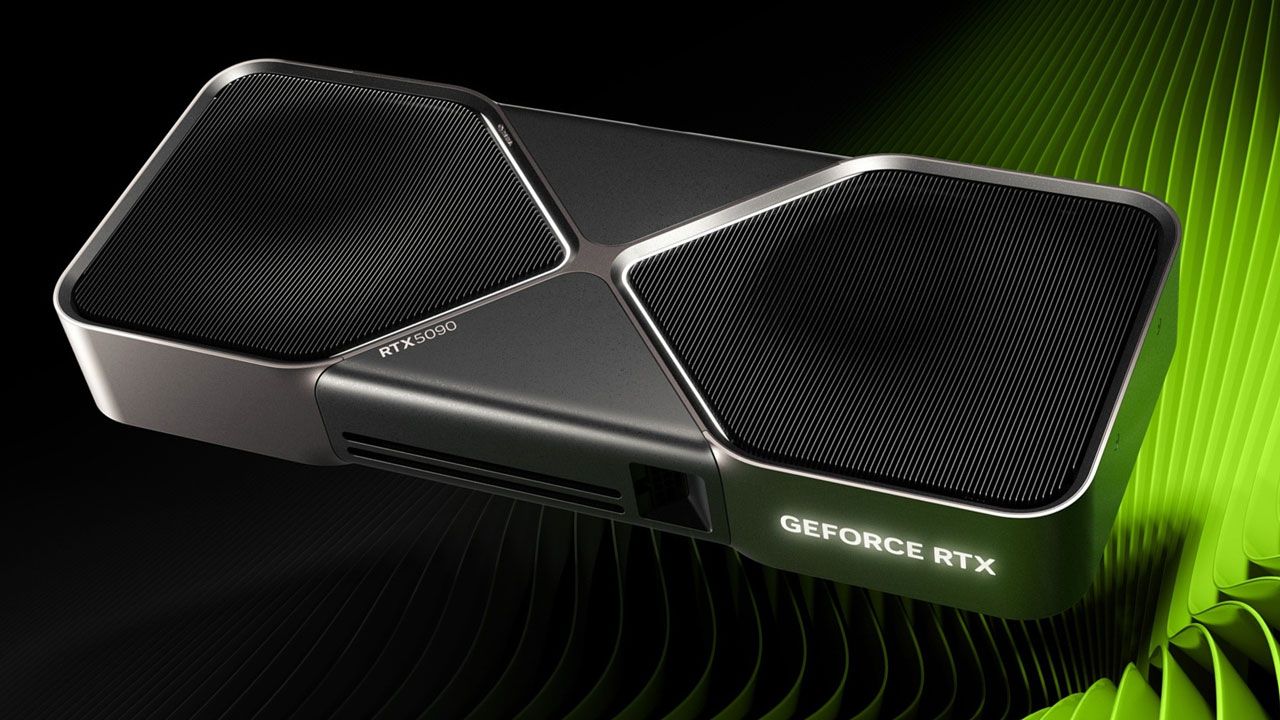
This one will be short and sweet. So remember how there are apparently no more RTX 5090s available most anywhere, even though Nvidia's Senior Vice President just said that the company definitely hasn't stopped making them? If you had been saving up for Nvidia's greatest card, there's still hope for you. Best Buy has an MSI Infinite ZS in stock with an RTX 5090 ensconced within for $7,599, making for roughly $5,300 for the RTX 5090 and $2,300 for the rest of the PC.

Yes, over five grand is definitely a lot to ask for a graphics card, but it's worth ponying up the cash if you want the best gaming card in recent years (and likely future, too). Besides, it's not like these will be in stock anytime soon (if ever), and they were commanding $7,500 or more in stores before they vanished.

Infinite ZS Gaming Prebuilt w/ RTX 5090: was $7799 now $7599
The MSI Infinite ZS prebuilt with a Nvidia RTX 5090 and a Ryzen 9950X3D CPU is probably one of the last few chances of getting ahold of the mighty GPU for anything resembling an acceptable price.View Deal

The rest of the PC around the humongous card is equally powerful. The Ryzen 9 9950X3D ($670) is probably the best desktop CPU in the current market, offering a high core count of 16 cores and 32 threads, fast clocks with a 5.7 GHz turbo speed, and 128 MB of cache. It'll run games and heavy applications with equal aplomb.

That chip sits atop an MSI B840-VC motherboard ($250 est.) with PCIe 5.0 support thanks to its AMD B840 chipset. An MSI CoreLiquid 360mm CLC ($110) keeps the processor cooled. There are 32 GB of RAM ($450 est.) on tap — though MSI doesn't mention the speed, 6000 MT/s is a good, reasonable guess for a high-end machine.

The machine is powered by an unspecified MSI 1300W Gold PSU ($170 est.), and all the hardware sits inside a MSI MEG Prospect 700RL case ($250 est.). A Windows 11 Home license currently sets you back about $130. For those keeping track at home, the PC core goes for over $2300. There are no weak spots we could find, too — pre-builts often skimp on one of their core parts, but there are no shortcuts here.

  •  

Nvidia reportedly insists the RTX 5090 isn't dead despite severe shortages and removed listings at multiple retailers

Last week, gamers still holding any hope that the GPU market would somehow stabilize had their hopes dashed. A while after Nvidia reportedly put the RTX 50 Super series on hold, rumors started flying that production of the already-rare RTX 5090 was stopping, likely to use precious silicon manufacturing capacity for more AI accelerators. Now, the company's senior VP Jeff Fisher reportedly said that card was not discontinued and would continue to be shipped. The statement comes after a myriad of websites, including Tom's Hardware, have asked the company for official comment, but to no avail.

The information comes from Taiwanese websites including 4Gamers and SJTV, which both are quoting a purported post-event interview where Fisher offered a brief explanation of the situation. According to the VP, supplies of the GPU are limited, but Nvidia is seemingly going all out to get the product to market (paraphrased from the Taiwanese reports).

"The supply chain (capacity) is indeed somewhat constrained, but NVIDIA is doing everything it can to get the product on the market. Although there are other variants of the RTX 5090 (chip), production has not been discontinued, and NVIDIA will continue to ship, which is very important," Fisher reportedly said to 4Gamers.

He also reportedly reiterated a common quote from Nvidia execs, stating that without GeForce, Nvidia wouldn't be where it is today, and likewise, the AI market wouldn't exist as it does today.

The claim that the card isn't gone after all merits some spot-checking, so we did a cursory browse of the common retailers. At Amazon, RTX 5090s are selling for about $8,500, but from third-party sellers. Best Buy has a grand amount of naught cards on offer, while Newegg lists 5090s for about $7,300, but from what are likely Chinese sellers, judging by the shipping time. The ever-famous U.S. tariffs would likely add quite a chunk of change to that price tag, too. Finally and perhaps most poignantly, the card remains absent from Nvidia's own marketplace and Micro Center as of this writing.

Some would say that these statements are nothing but a means to keep the company in gamers' minds, even though gaming-related revenue is now a vanishingly small piece of Nvidia's ever-larger money pie.

Jensen's firm isn't the only one seemingly keeping up appearances, as Intel has repeatedly stated that its long-awaited refresh of consumer GPUs isn't dead, and last year AMD said it still intends to deliver "the best mainstream gaming GPUs on the market." Yet there are no new GPU launches from any of the three, and their quarterly launch figures keep doubling down on AI.

We reached out to Nvidia for comment on the situation and received no reply.

  •  

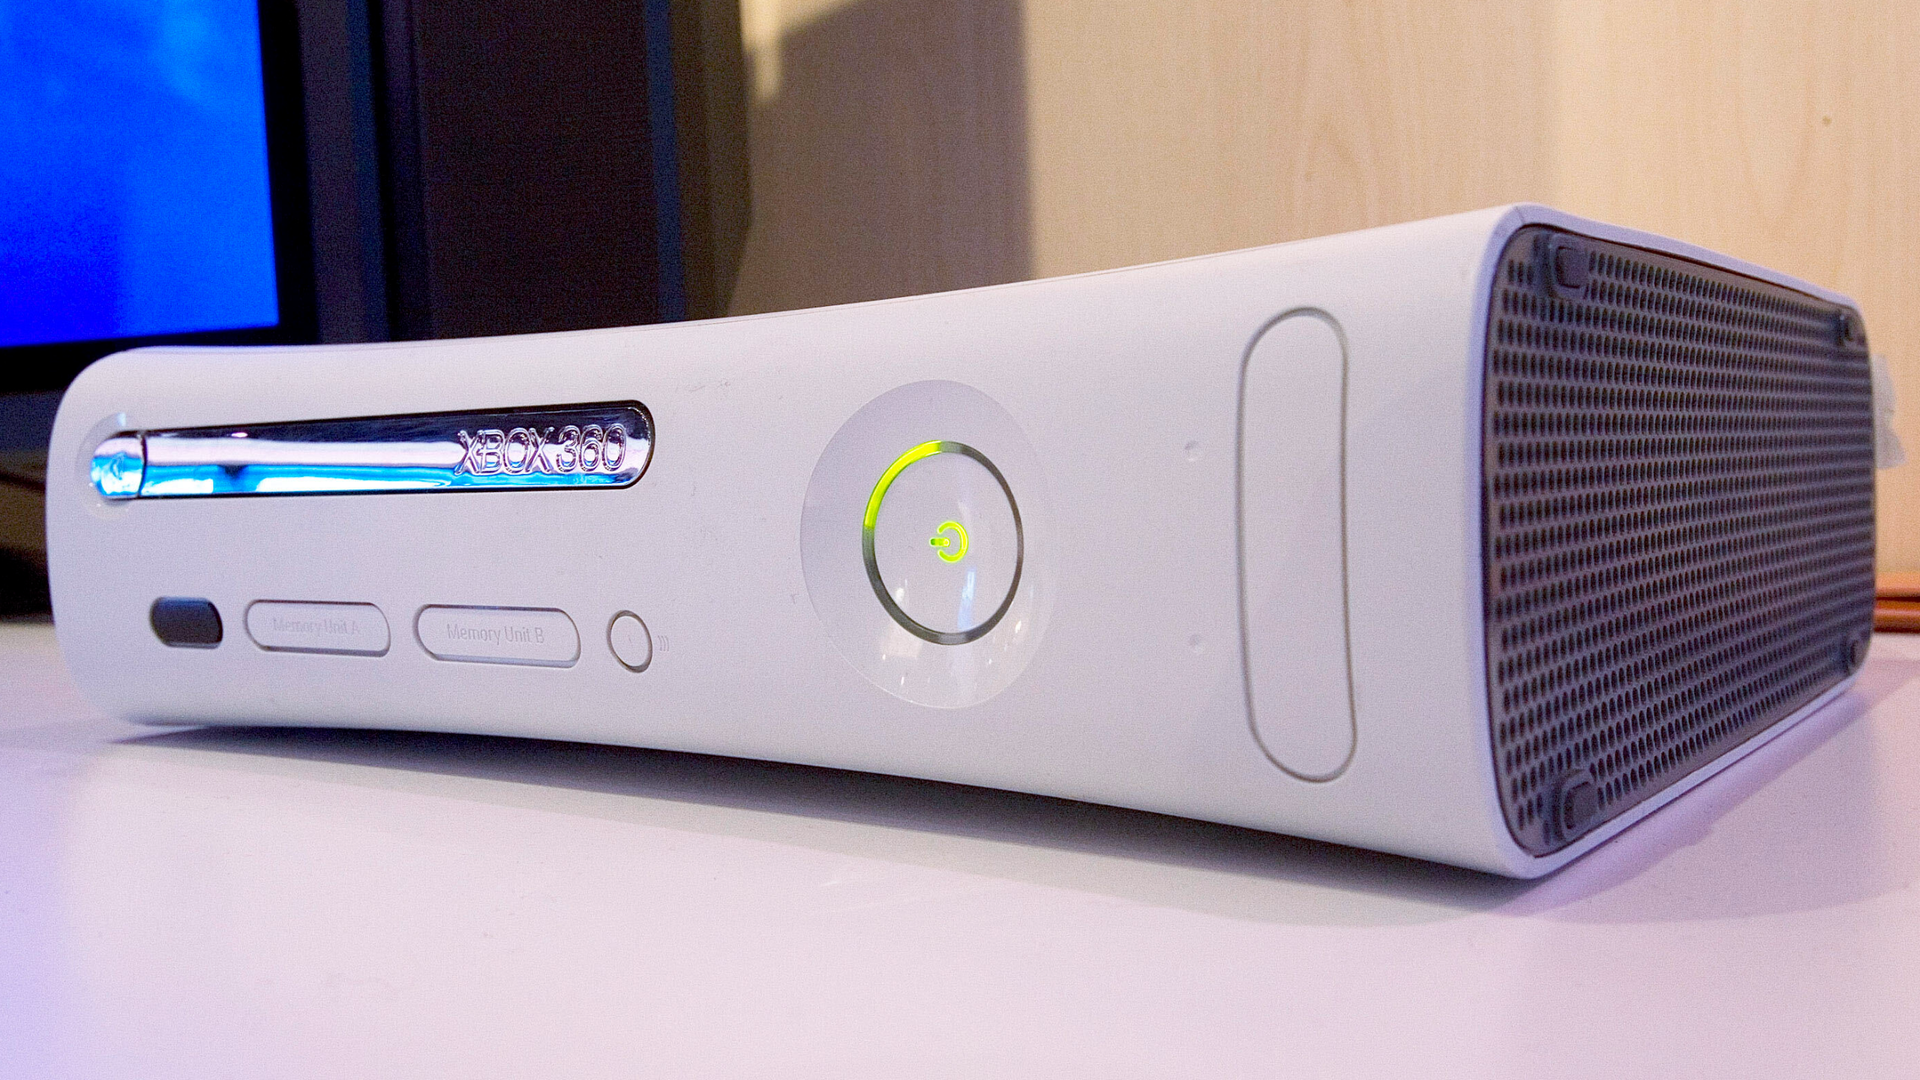
Modder finishes nine-year Xbox 360 voltage glitch mod with a $4 microcontroller, cracks the console open

The Xbox 360 has been cracked open multiple times over the years, and almost every time Microsoft's updates plugged whichever hole let hackers through. The first method was modded DVD firmware in 2006, a hypervisor hack followed in 2007, and a wiring hack exposing JTAG debugging ports was revealed in 2009. The longest-lasting physical hack was 2011's CPU force-reset exploit. That maneuver needed specialized hardware along with a voltage-glitching chip, but an enterprising techie showed how it can be performed nowadays with the assistance of a Raspberry Pi Pico, costing all of $4 (or about 5€ / £5). The crack marks the culmination of a nine-year effort by the modder.

To get the elephant out of the room, yes, just last week the PeerPressure Xbox 360 persistent soft-mod was released. But we're here to talk signals and wires. The aforementioned reset exploit involves sending a teeny weeny tiny signal directly into the CPU's reset pin. You'd think this would do what it says on the label, but what happens instead is that the CPU executes the current instruction incorrectly.

Naturally, someone figured out how to leverage that to run any code on the CPU, thus completely bypassing Microsoft's impressive and frankly rather effective layers of cryptography within the console. Sending said signal for an effective hack, though, requires spectacularly precise timing with a resolution down to nanoseconds, and glitch-chips may even require several attempts to get a successful "latch."

Joshua Kennedy, a Scottish hacker, bought a Matrix Coolrunner Rev D modchip board back in 2017 to hack his console this way, but it required soldering wires, NAND, and programmers, and patience. He once tried rolling his own programmers using an old PC's parallel port (a common substitute), but never got the project off the ground and shelved the idea.

Fast-forward to 2026, and a new tool presented itself: the highly successful Raspberry Pi Pico, a highly capable microcontroller-on-a-stick, whose price starts at all of $4. Armed with this, he started the procedure. He connected the Pi Pico to the NAND interface header on the console to be able to dump the console's NAND flash firmware — a task easily accomplished with just some wiring and the PicoFlasher utility. Although the post doesn't mention it, Kennedy likely took the NAND data, patched it with XeLL, and reuploaded it.

He moved on to download Octal450's Timing Files, a set of mini-programs triggering the glitch chip at the best possible timing to try and reset the CPU. These are necessary because the window of opportunity is different across every hardware revision of the Xbox 360. Enlisting the Pi Pico once again, he uploaded the timing files to the Matrix Coolrunner, and presumably ran the rest of the hack process. And thus the task was complete, and "a project that defeated [Kennedy] in 2017 was made trivial in 2026 by a £5 microcontroller."

  •  

Linus Torvalds posts his first AI-assisted patch to the Linux kernel, synthetic test clocks 23x performance leap

After a few revisions of his position on AI-assisted contributions to the Linux kernel, Linus Torvalds has posted his own first LLM-assisted patch. The development branch purports to fix an old issue with massive cache contention when many CPUs are reading the same file — a scenario potentially encountered when using shared libraries, databases, and web servers. Several developers had already made attempts over the years at fixing the issue, all with varied results, none quite ideal as an all-encompassing solution.

Torvalds posted his own draft for solving the problem in early 2024, and has used it on his own laptop since that time. However, he recently took the plunge and decided to "try to actually solve this thing using an LLM." He's now posted his solution in a development branch, and claims that he's seen a 23x performance improvement in a dedicated synthetic benchmark, though he notes that actual real-world impact will be far less significant, as "no real load" will witness those figures. If we had to guess, this improvement would benefit server workloads far more than desktop machines.

Over time, Torvalds has broadly taken a pro-AI stance on LLM tooling, at least within the purview of the tightly controlled, review-heavy environment of the Linux kernel code. Last July, he stated he's "willing to absolutely put [his] foot down" on AI haters, pointing out that an automated code review tool the kernel team uses outperforms humans, and that it caught basic programming mistakes that shouldn't have been submitted in the first place.

The team is even changing its policy to no longer require that patch authors disclose they used an AI tool when generating their code. Torvalds once again took an assertive stance, reiterating that users should treat LLMs as yet another tool, likening it to compilers or editors. In his view, he simply expects that "people do their best and [...] understand what they are doing."

Some might say that few people in the world are better-suited to properly employ an LLM than Torvalds, and by extension, kernel maintainers. There's an entire universe of difference between a senior master programmer using the LLM to speed up the boring parts of his work, and some newbie with a credit card going "claude make linux faster plz no mistakes."

However, It's not all roses. Thanks to how adept AI agents have become at recognizing common security flaw patterns, the Linux security mailing list became "unmanageable" earlier in the year. Linux has been fixing CVEs at an astonishingly rapid pace of around 2,000 per release. Still, the team's hand is being forced into dropping older hardware drivers, as they're often the target of numerous security reports, despite their negligible install base.

  •  

Russian chipmakers demo homegrown RISC-V and Arm chips with retro games

Geopolitics and sanctions have mostly cut off the Russian public from Western hardware — at least officially. In recent ages, the country's homegrown chip designs are Arm, RISC-V, and Elbrus architectures. A handful of interesting designs were on display at the Microelectronics 26 (ME26) forum in Sochi, using retro gaming as a demonstration point. A couple of years back, the government even issued an order to create a high-end gaming console, albeit with relatively little success. The result of that initiative didn't appear to be on display at the event.

На выставке МЭ26 в Сочи показывали сразу несколько игровых применений русских процессоровБайкал: консоль и визитка на Ушке BE-U1000Элвис: полноценная приставка на Гиперком У (бывш. СКИФ)МЦСТ: «игровые» ПК на ЭльбрусахНе серьёзно, но занимательно#riscv #innoru #pureru https://t.co/QGlRTMnvLROctober 11, 2026

The report comes from Dmitrii Kuznetsov, a RISC-V and Rust enthusiast who displayed photos from the event. The first units on display use Baikal Electronics' BE-U1000 microcontroller. According to our digging, the chip packs a CPU with three CloudBear cores (32-bit RISC-V) — two BR-350s clocked at 200 MHz, along with a BM-310 at 100 MHz.

Given the microcontroller nature, embedded resources are intentionally sparse, with 256 KB of flash and 192 KB of SRAM — though there's support for external flash. A host of I/O interfaces, including USB 2.0, I2C, I2S, UARTs, and 48 GPIO lines, round out the 10x10 mm QFN-88 package. These parts are seemingly aimed at robotics, automation, IoT, sensors, and similar applications.

There was a business card-sized controller-and-console on display with a BE-U1000 chip, along with an "Ushka" console styled like the original NES (with matching controllers). The game on display appears to be Chip 'n Dale: Rescue Rangers.

Next up, there's the Elvis Hypercom-U, a SoC packing four Arm Cortex-A53 CPU cores at up to 1.2 GHz, dual ELcore-50 DSPs, a PowerVR GE8300 GPU, and dedicated video, image, and navigation processing blocks. The main silicon can be paired with up to 8 GB of LPDDR4, and supports USB 3.0, Gigabit Ethernet, Wi-Fi, and Bluetooth connectivity, and HDMI output.

This product is apparently aimed at multimedia, navigation, SBCs, and smart cameras. At the show, a board with the Hypercom-U was shown playing the original Super Mario as a demonstration.

Finally, there were MCST's Elbrus-based PCs, though the tweeter offered few details on which were on display. For context, Elbrus is a Russian-developed chip architecture, often poised as the basis for high-end desktop and server applications.

Our best guess is that the machines at the forum were based on the leading-edge Elbrus-16S chip with 16 cores at up to 2 GHz and up to 8 channels of DDR4-3200 RAM. The chip is manufactured on a 16 nm process and comprises 12 billion transistors. There are dual-processor server prototypes with up to 2TB of RAM using this design.

The other chip likely being demoed is the Elbrus-2S3, a chip targeted at mini-PCs and laptops. We've covered the Rostec MP21 previously, a Raspberry Pi-like machine with 8GB of RAM and SSDs up to 480GB. The 16-nm SoC is fairly decent, clocked at up to 2 GHz and capable of 196 GFLOPS. There's support for DDR4-3200 and PCIe 3.0, but power consumption can be fairly nasty, as the MP21 board can chew around 40W.

  •