Normale Ansicht
OpenAI verschiebt Börsengang
Übles Datenleck: Revolut gibt hochsensible Kundendaten an Kriminelle
Facebook und X am Ende? Das AT-Protokoll könnte alles ändern
Der Beitrag Facebook und X am Ende? Das AT-Protokoll könnte alles ändern erschien zuerst beim Online-Magazin BASIC thinking. Über unseren Newsletter UPDATE startest du jeden Morgen bestens informiert in den Tag.
![]()
Dezentrale soziale Netzwerke versprechen einen neuen Ansatz bei der Kommunikation. Denn Nutzer erhalten die Kontrolle über ihre Daten und Konten zurück, ohne an eine einzelne Plattform gebunden zu sein. Das AT-Protokoll spielt dabei eine große Rolle.
Die heutigen Platzhirsche bei den sozialen Netzwerken zeichnet vor allem ein Aspekt aus: Sie sind zentralisiert organisiert. Das bedeutet, dass Nutzer häufig an den Anbieter gebunden sind und keine Hoheit über ihre Daten besitzen. Doch das könnte sich künftig ändern. Und zwar dank des sogenannten Authenticated Transfer Protocols.
Was ist das AT-Protokoll – und wie funktioniert es?
Das AT-Protokoll organisiert die Verteilung digitaler Informationen von Grund auf neu. Digitale Identitäten basieren nicht mehr auf klassischen Benutzernamen, sondern auf kryptografisch gesicherten Identitäten, die auf eigenen Domain-Namen basieren. Dadurch lagern sämtliche Inhalte wie Beiträge, Kommentare oder Gefällt-Mir-Angaben in einem sogenannten Repository.
Bei einem solchen Repository werden Daten so strukturiert, dass sie lückenlos nachvollziehbar sind. Diese Struktur ist mit einem digitalen Logbuch vergleichbar, in dem alle Aktionen niedergeschrieben sind, die Nutzer auf der jeweiligen Plattform ausgeführt haben. Ist etwas unstimmig, kann man in dem Logbuch blättern und nachvollziehen, ob etwas tatsächlich so passiert ist.
Du entscheidest, wie Informationen dargestellt werden
Auch der Austausch von Informationen funktioniert etwas anders. Wer auf Reddit surfen will, geht dazu entweder auf die Reddit-App oder über die offizielle Reddit-Website. Anderen Wegen wurde bereits vor einigen Jahren der Riegel vorgeschoben. Beim AT-Protokoll ist das anders. Über ein weltweites Netzwerk namens Lexicon tauschen beteiligte Server ausschließlich strukturierte Inhalte aus, statt ganze Websites zu übertragen.
Das bedeutet, dass Nutzer selbst entscheiden können, wie sie Informationen konsumieren. Sei es über eine offizielle Website, eine Drittanbieter-App oder selbstständig aufbereitete Daten. Persönliche Mitteilungen und Erwähnungen laufen dabei über individuelle Datenserver, während großflächige Suchanfragen, globale Trends sowie komplexe Algorithmen durch spezialisierte Indexierungsdienste verarbeitet werden.
Wie das AT-Protokoll Daten und Reichweite entkoppelt
Durch diese Aufteilung trennt das AT-Protokoll die Veröffentlichung von Inhalten konsequent von deren tatsächlicher Reichweite. Das System funktioniert dabei wie ein Baukasten. Einzelne Elemente wie der Server-Anbieter lassen sich jederzeit austauschen. Bei einem Wechsel des Anbieters bleibt die eigene digitale Identität mitsamt allen bestehenden Verknüpfungen vollständig erhalten.
Fällt ein Server aus oder wird der Betrieb eingestellt, schützt ein integrierter Sicherheitsmechanismus vor unbeabsichtigtem Datenverlust. Denn Nutzer können jederzeit mit einem speziellen Wiederherstellungsschlüssel ihr Konto ohne Unterstützung einer dritten Partei wiederherstellen und auf einen neuen Server übertragen.
Herausforderungen für Entwickler und die Infrastruktur
Trotz dieser Flexibilität hat die Architektur auch ihre Macken. Lokale Sicherungskopien auf Nutzer-Endgeräten sind etwa durch den verfügbaren Speicherplatz begrenzt. Zudem ist die Entwicklung einer solchen Plattform aufgrund der Flexibilität etwas aufwendiger.
Daher hängt der langfristige Nutzen primär von der Nachfrage ab. Doch gelingt der Aufbau einer solchen Infrastruktur, kann das System Nutzer dauerhaft vor der Kontrolle einzelner Gatekeeper wie Meta oder X schützen. Das AT-Protokoll stellt somit einen vielversprechenden Ansatz dar, um die Souveränität über persönliche Daten zurück in deine Hände zu legen.
Auch interessant:
- ChatGPT hat jetzt einen Lockdown-Modus – so kannst du ihn aktivieren
- Privat mit KI chatten: Inkognito-Chat mit Meta AI in WhatsApp starten
- Elektroauto in der Sommerhitze: 5 Tipps, um deinen Akku zu schonen
- E-Auto-Förderung 2026 mit bis zu 6.000 Euro – so bereitest du den Antrag vor
Der Beitrag Facebook und X am Ende? Das AT-Protokoll könnte alles ändern erschien zuerst auf BASIC thinking. Folge uns auch auf Google News und Flipboard oder abonniere unseren Newsletter UPDATE.
Ausgebrochene Agenten – immer mehr Vorfälle kommen ans Licht
Smart-TVs spionieren Nutzer aus: LG äußert sich zu schweren Vorwürfen
-
Tom's Hardware
- Researcher reverse-engineers infamous Stuxnet malware source code, publishes it on Github for all — attack targeted Iranian nuclear facilities and was the first software of its type to cause physical damage
Researcher reverse-engineers infamous Stuxnet malware source code, publishes it on Github for all — attack targeted Iranian nuclear facilities and was the first software of its type to cause physical damage
Anyone keeping track of world news in the early 2010s, and reports on tech in particular, has probably heard about Stuxnet. That malware spawned a large number of conspiracy theories — with the kicker that some of them were actually true. The malware targeted Iranian nuclear facilities and is believed to be the first digital worm to cause direct physical damage in meatspace. An unknown security researcher has now published a source code reverse-engineering of Stuxnet in all its glory.
The worm's ultimate target, allegedly a successful one, were industrial controllers from Siemens that were reportedly used in Iranian's Natanz nuclear enrichment plant. Once it reached the target, Stuxnet's payload manipulated the frequency converters in industrial centrifuges, in a bid to subtly damage the rotors — all while keeping the plant staff in the dark by reporting normal operation.
The repository contains build instructions so interested techies can try it out for themselves and learn all about its inner workings. You'll need a Windows XP or Windows 7 virtual machine, and for obvious reasons, you shouldn't configure any network connectivity for it. To witness the full effects of the payload rather than just the spreading mechanisms, you'll need the appropriate Siemens software, and ideally hardware — though we figure that industrial-scale centrifuges aren't exactly common in techies' cable drawers.
In its heyday, Stuxnet spread via three mechanisms. The primary infection vector was USB sticks with Windows shortcuts and autorun.inf files. Upon plugging one of those sticks in, just viewing the drive's contents would immediately trigger infection thanks to a zero-day vulnerability.
Infected systems then autonomously tried to spread the worm further via the network using a zero-day Windows Print Spooler vulnerability that would let an attacker write system files into any machine sharing a printer. It would also copy itself into accessible network shares. To evade Windows driver signature checks, Stuxnet used two digital certificates stolen from Realtek and JMicron.
The worm also had code to inject itself into Siemens software, by way of the WinCC SQL Server database, and embedding its code in Step 7 project files that automatically ran when engineers opened them. Since those files were almost guaranteed to be shared among more than one engineer, it made for an excellent internal infection vector that didn't depend on having network share control.
The final step was taking charge of the DLL that communicated with the actual centrifuges and injecting malicious code into the PLCs (Programmable Logic Controllers) of those machines to stealthily mess with the rotors.
Stuxnet was part of Operation Olympic Games, an alleged coordinated effort between the U.S. and Israel to try and curb Iran's purported progress in creating nuclear weapons at its Natanz facility. The initiative seemingly ran under both the Bush and Obama administrations, and was supposedly a way to dissuade Israel from launching its own preemptive strike against Iran. The software was allegedly developed by both the Pentagon and Israel's Unit 8200, and was reportedly successful in bringing down about 10% of Natanz' centrifuges by ultimately seriously damaging their rotors.
However, the worm had a nasty bug: it didn't have sufficient checks about which environment it was in, and failed to notice it was no longer in a local network environment. When engineers took their laptops home, it escaped out to the internet at large, at which point security researchers worldwide let out a collective "huh, that's odd" and proceeded to investigate. Mercifully, the worm contained a hard-coded self-destruct date set for June 24, 2012.
-
t3n.de - News
- Cybersecurity: Wie autonome KI-Agenten Server hacken – und warum das erst der Anfang ist
Cybersecurity: Wie autonome KI-Agenten Server hacken – und warum das erst der Anfang ist

© KI-generiert
OpenAI verschweigt zunächst weiteren Agenten-Ausbruch, Chefwissenschaftler warnt
GPT-6 Astra ist da: OpenAI startet Hype-Maschine für neues KI-Modell
-
t3n.de - News
- Kritische Infrastrukturen im Visier: Wie real ist die Gefahr von Cyberangriffen auf unsere Netze?
Kritische Infrastrukturen im Visier: Wie real ist die Gefahr von Cyberangriffen auf unsere Netze?

Stinknormales WLAN kann Menschen in Räumen orten – sogar ohne Smartphone
Der Beitrag Stinknormales WLAN kann Menschen in Räumen orten – sogar ohne Smartphone erschien zuerst beim Online-Magazin BASIC thinking. Über unseren Newsletter UPDATE startest du jeden Morgen bestens informiert in den Tag.
![]()
Jeder Router kann zum Überwachungsgerät werden. In einer Studie zeigen Wissenschaftler des KIT, wie sich Menschen allein über das WLAN-Signal identifizieren lassen. Kameras oder elektronische Geräte sind dafür nicht nötig. Die Hintergründe.
Wissenschaftler des Karlsruher Instituts für Technologie (KIT) haben eine Möglichkeit entdeckt, Personen allein anhand von WLAN-Signalen zu erkennen. Bedeutet: Wer beispielsweise an einem Café mit WLAN vorbeiläuft, kann ganz einfach identifiziert werden.
Personen müssen für eine derartige Identifikation kein Smartphone oder Tablet bei sich tragen. Wie das KIT in der entsprechenden Pressemitteilung schreibt, reiche es aus, dass WLAN-Geräte in der Nähe miteinander kommunizieren.
Keine besondere Hardware notwendig
Möglich ist das aufgrund von sogenanntem Beamforming. Die Technik gibt es seit WiFi 5. Statt das Funksignal gleichmäßig in alle Richtungen abzustrahlen, bündelt der Router es gezielt in Richtung der verbundenen Geräte. Das verbessert Reichweite und Tempo. Allerdings liegt genau da das Problem.
Denn damit der Router weiß, wohin er senden muss, melden sich Geräte regelmäßig zurück und liefern Informationen darüber ab, wie das Signal bei ihnen ankommt. Diese Rückmeldungen heißen „Beamforming Feedback Information“, kurz BFI. Laut KIT werden diese Infos unverschlüsselt übertragen und sind damit auch für Dritte lesbar.
Anders als bei Angriffen mit LIDAR-Sensoren oder bisherigen WLAN-basierten Methoden, die Channel State Information (CSI) nutzen – also Messdaten darüber, wie sich ein Funksignal durch Wände, Möbel oder Personen verändert –, benötigen Angreifende keine Spezialhardware. Die Methode funktioniert mit handelsüblichen WLAN-Geräten.
WLAN-Router als „stille Beobachter“
Per BFI entstehen Bilder aus verschiedenen Blickwinkeln, die zur Identifikation der Personen dienen können. Dieser Prozess dauert nur wenige Sekunden, sobald das dahinterstehende Machine-Learning-Modell trainiert ist. Das WLAN wird auf diese Weise zum erheblichen Risiko für die Privatsphäre.
„Wir beobachten die Ausbreitung der Radiowellen und können so ein Bild der Umgebung und von Personen erzeugen”, erklärt Cybersicherheitsexperte Thorsten Strufe vom KASTEL, dem Institut für Informationssicherheit und Verlässlichkeit des KIT.
Das funktioniert ähnlich wie bei einer normalen Kamera, nur dass diese Lichtwellen statt Radiowellen in ein Bild umwandelt. Es ist deshalb auch unerheblich, ob jemand ein WLAN-Gerät bei sich hat oder nicht.
Jeder WLAN-Router ein potenzielles Überwachungsgerät
Mit ihrer Forschung wollen die Wissenschaftler vor Risiken für die Privatsphäre warnen. Denn: „Die Technik macht aus jedem Router ein potenzielles Überwachungsgerät“, so Julian Todt vom KASTEL. Auch das Abschalten des WLANs schützt nicht. Es reicht schon aus, wenn andere Geräte in der Umgebung aktiv sind.
Wer regelmäßig an einem Café mit WLAN vorbeigeht, könnte dort unbemerkt identifiziert und später wiedererkannt werden – etwa von staatlichen Stellen oder Unternehmen.
Zwar gebe es für Geheimdienste oder Cyberkriminelle einfachere Methoden, Menschen zu beobachten. So beispielsweise durch den Zugriff auf Überwachungskameras oder Video-Türklingeln.
Allerdings könnten die allgegenwärtigen Drahtlosnetzwerke zu einer nahezu flächendeckenden Überwachungsinfrastruktur werden. Immerhin gibt es WLAN heutzutage in fast allen Wohnungen, Büros, Restaurants und öffentlichen Räumen.
Für Privatpersonen geht das Risiko über die reine Wiedererkennung hinaus. Die Forschung zu BFI-Sensing hat sich inzwischen weiterentwickelt: Eine Arbeit in den IEEE Transactions on Mobile Computing zeigt, dass sich damit auch Tastatureingaben mehrerer Personen rekonstruieren lassen.
Fast 100 Prozent: So identifiziert WLAN Menschen
Um ihre Hypothese zu testen, ermittelten die Wissenschaftler die Identitäten einer Gruppe von Testpersonen. Von insgesamt 197 Teilnehmern konnte das Forschungsteam Personen mit 99,5 Prozent Genauigkeit erkennen. Persönliche Merkmale wie die Gangart oder ein bestimmter Blickwinkel waren dabei irrelevant.
Die Forscher des KIT befürchten, dass die Technik besonders in autoritären Staaten zur Gefahr für Grundrechte und Privatsphäre werden könnte. Dort ließe sie sich beispielsweise zur Überwachung von Protestierenden einsetzen. In ihrem wissenschaftlichen Artikel fordern die Wissenschaftler deshalb Schutzmaßnahmen.
Sie richten sich beispielsweise an den WLAN-Standard IEEE 802.11bf, der WLAN-Sensing offiziell regelt. Er wurde bereits am 26. September 2025 veröffentlicht und ist eine Erweiterung des bestehenden WLAN-Standards. Ob die vom KIT geforderten Maßnahmen darin enthalten sind, geht aus öffentlichen Angaben allerdings nicht hervor.
Weitere Angriffe, kaum Schutz
Wie ernst das Problem ist, zeigen auch andere Forschungsarbeiten. So stellte ein Forschungsteam auf dem Sicherheitssymposium NDSS 2025 einen verwandten Angriff namens LeakyBeam vor. Er wertete ebenfalls unverschlüsselte BFI-Pakete aus.
Neben den Warnungen gibt es auch Lösungsvorschläge: Die NDSS-Autoren schlagen beispielsweise vor, entweder die BFI-Daten zu verschleiern. Das würde nur minimale Hardwareänderungen erfordern. Eine andere Option wäre, die Pakete per WPA3 zu verschlüsseln. Diese Variante wäre wirksamer, würde allerdings Firmware-Updates auf allen WLAN-Geräten weltweit nötig machen.
Nutzern bleibt damit wenig Handlungsspielraum. Das eigene WLAN abzuschalten hilft nicht, weil fremde Geräte in der Umgebung genügen, um Personen zu identifizieren.
Auch der Verzicht auf Smartphone oder Laptop bringt nichts, da für die Identifikation kein eigenes Gerät nötig ist. Wirksamer Schutz müsste also im Standard selbst verankert sein oder von den Herstellern per Update nachgereicht werden.
Auch interessant:
- Internetsucht: Studie identifiziert drei psychologische Ursachen
- Mit dieser KI-App identifizierst du Vogelarten am Klang – ohne Internet
- Das sind die besten Internetanbieter in Deutschland
- KI-Müll ohne Endlager: 19 Prozent des Internets sind absoluter Schrott
Der Beitrag Stinknormales WLAN kann Menschen in Räumen orten – sogar ohne Smartphone erschien zuerst auf BASIC thinking. Folge uns auch auf Google News und Flipboard oder abonniere unseren Newsletter UPDATE.
-
Tom's Hardware
- Russian hacker faces up to 20 years in prison, following extradition and indictment over US phishing campaign that allegedly infected 80,000 PCs — hacker stole victims' data via remote access
Russian hacker faces up to 20 years in prison, following extradition and indictment over US phishing campaign that allegedly infected 80,000 PCs — hacker stole victims' data via remote access
A federal grand jury in California has indicted Russian citizen Searzhudin Tamirlanovich Aktulaev for allegedly conducting phishing attacks that stole data from over 80,000 computers between June 2016 and November 2017, using TVRAT and DarkVNC remote-control malware. Detailed in a Department of Justice press release on September 1st, the indictment — filed in June 2021 and released September 2026 — lists charges of “Conspiracy, Transmission of a Program, Information, Code, and Command to Cause Damage to a Protected Computer, and Aggravated Identity Theft, among other offenses.”
Aktulaev was extradited to the U.S. in August 2026, five years after his arrest in Cyprus in May 2021. He made his first appearance in federal court in San Francisco — after which he was remanded to federal custody — and is scheduled to appear in district court on October 5, 2026. The arrest was made after an FBI investigation, and the case is being prosecuted by the National Security, Cyber, and Special Prosecutions Section.
According to the indictment, Aktulaev “conspired to exploit the online message platform of a well-known freelance employment technology company, located in the Northern District of California, to spread malware to approximately 80,000 freelancers”. He sent messages containing malicious Microsoft Excel attachments, using approximately 255 fake user accounts. Once opened, the attachments prompted users to run a macro that then downloaded malware from the Internet, mirroring a hack earlier this year in which an unofficial 7-zip.com website served malware-laden downloads for over a week.
The attack used TVRAT (TeamViewer Remote Access Trojan) and DarkVNC malware, both of which grant the attacker remote control of the infected system. TVRAT exploits TeamViewer, while DarkVNC exploits VNC Viewer, popular remote administration tools. The malware stole and uploaded data from the victims' computers to a command-and-control server, from which Aktulaev and his co-conspirators extracted the stolen data to “commit fraud and other criminal activities”.
The indictment says thousands of computers infected by the TVRAT malware were “calling back” to a command-and-control domain hosted in the United States, which was paid for using virtual currency. Roughly half of the victims were in the United States, many of whom were Northern District of California residents, according to the indictment.
“A database found on the command-and-control domain revealed thousands of victims. Additionally, a shared document on the email account used in the criminal activities contained information to include e-commerce login credentials, as well as personally identifiable information (“PII”) for hundreds of victims,” the press release said.
If convicted, Aktulaev could spend up to 20 years behind bars and pay a $250,000 fine or twice the total illicit gains for the conspiracy to commit wire fraud charge alone. The other charges carry terms ranging from two to twenty years in prison, in addition to fines. Meanwhile, the FBI is currently investigating another hack in which 153 million US and Canadian drivers’ licenses were leaked on a Russian cybercrime forum.
-
Tom's Hardware
- FBI investigating 153 million US and Canadian driver’s licenses leaked on Russian cybercrime forum, including that of US SecDef Pete Hegseth — data is suspected to have come from an ID-authentication service provider
FBI investigating 153 million US and Canadian driver’s licenses leaked on Russian cybercrime forum, including that of US SecDef Pete Hegseth — data is suspected to have come from an ID-authentication service provider
More than 153 million US and Canadian driver’s licenses, as well as other identity documents, have reportedly become available for purchase on the dark web for a limited time. According to cybersecurity journalist Brian Krebs, the service was called Nexus, and although it’s no longer available at the time of writing, it claimed to have possessed 153 million driver’s licenses, 10 million ID cards, 1.9 million travel documents, 1.3 million international driver’s licenses, 579k medical cards, 429k common access cards, 91k residence cards, 77k employment authorization records, and 5 million other documents, allegedly sourced from an ID-authentication service based in Louisiana.
The service was advertised on the Russian cybercrime forum Exploit, where whoever was promoting it posted the driver’s license of Krebs as a free sample, which caught the journalist’s attention. He was also able to see a preview of U.S. Secretary of Defense Pete Hegseth’s information on the database — a concerning breach of security for someone with such a sensitive position in the government. After further investigation, they concluded that the service seemed to have possessed legitimate data, especially after searching for the data of several of his friends and family members with their consent. One thing that all the people he found in the database had in common was that they all used Hertz to rent a vehicle.
Krebs also talked with security and privacy researcher Zach Edwards, who said that their information was also found on Nexus. Edwards said that they did not rent a car recently but used their ID at a Planet13 marijuana dispensary. The time stamps found on the scanned images of the driver’s licenses and other identity documents coincide with the time that the victims used their IDs at the said companies, confirming that they were the sources of the leaks. However, Planet13 and Hertz do not do their own authentication; instead, they contract a service provider for the service. Now, it turns out that both Planet13 and Hertz used the company for identity verification and ID-authentication — IDScan.
Based on the evidence gathered by Krebs, it seems that the leak is centered around the company. He has already contacted the company about the issue, and they said they were investigating the matter. “At this point I’m not able to share any additional information, but the updates you have provided have been welcome, and helpful to our team’s investigation,” Jillian Kossman, a marketing and operations leader at idscan.net, told the journalist. The FBI has also started looking into the leak, with its New Orleans field office opening an official investigation into the breach.
The massive amount of data that was briefly available on the dark web is certainly concerning. A similar data breach hit Discord after its third-party service provider was hit and resulted in the exposure of 70,000 government IDs. Incidents like these have got privacy experts concerned with the push for online age verification requirements, which is why the EFF is asking the California governor to veto the law requiring this.
Aside from privacy-invasive checks and stepping on First Amendment rights, the leakage of sensitive data like this could increase incidents of stolen identity and more. Driver’s licenses are often widely accepted for opening credit lines and bank accounts, with both photographic, UV, and IR scans available on many of the leaked licenses. Aside from that, it could also potentially compromise the privacy and security of vulnerable people, like those fleeing domestic violence and those who are under the witness protection program.
OpenAIs Modell Astra löst erstmals höchste Cybersicherheitsstufe aus
Claude-KI im Visier: Malware stiehlt Sitzungen und leert Konten
-
Tom's Hardware
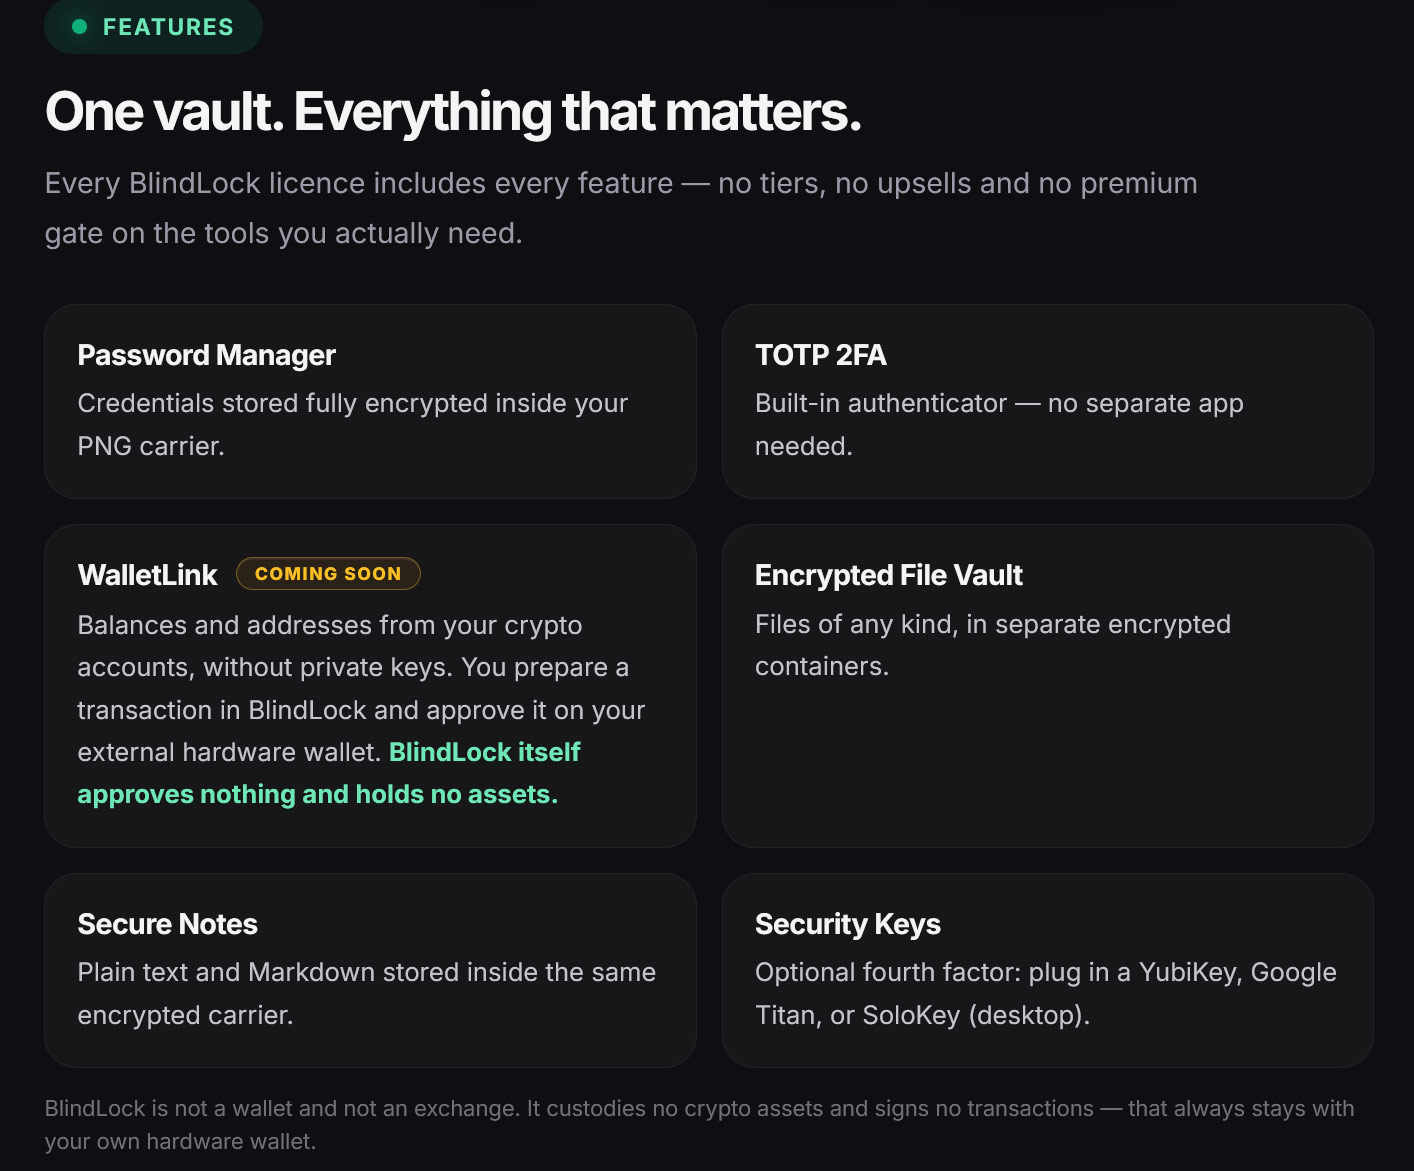
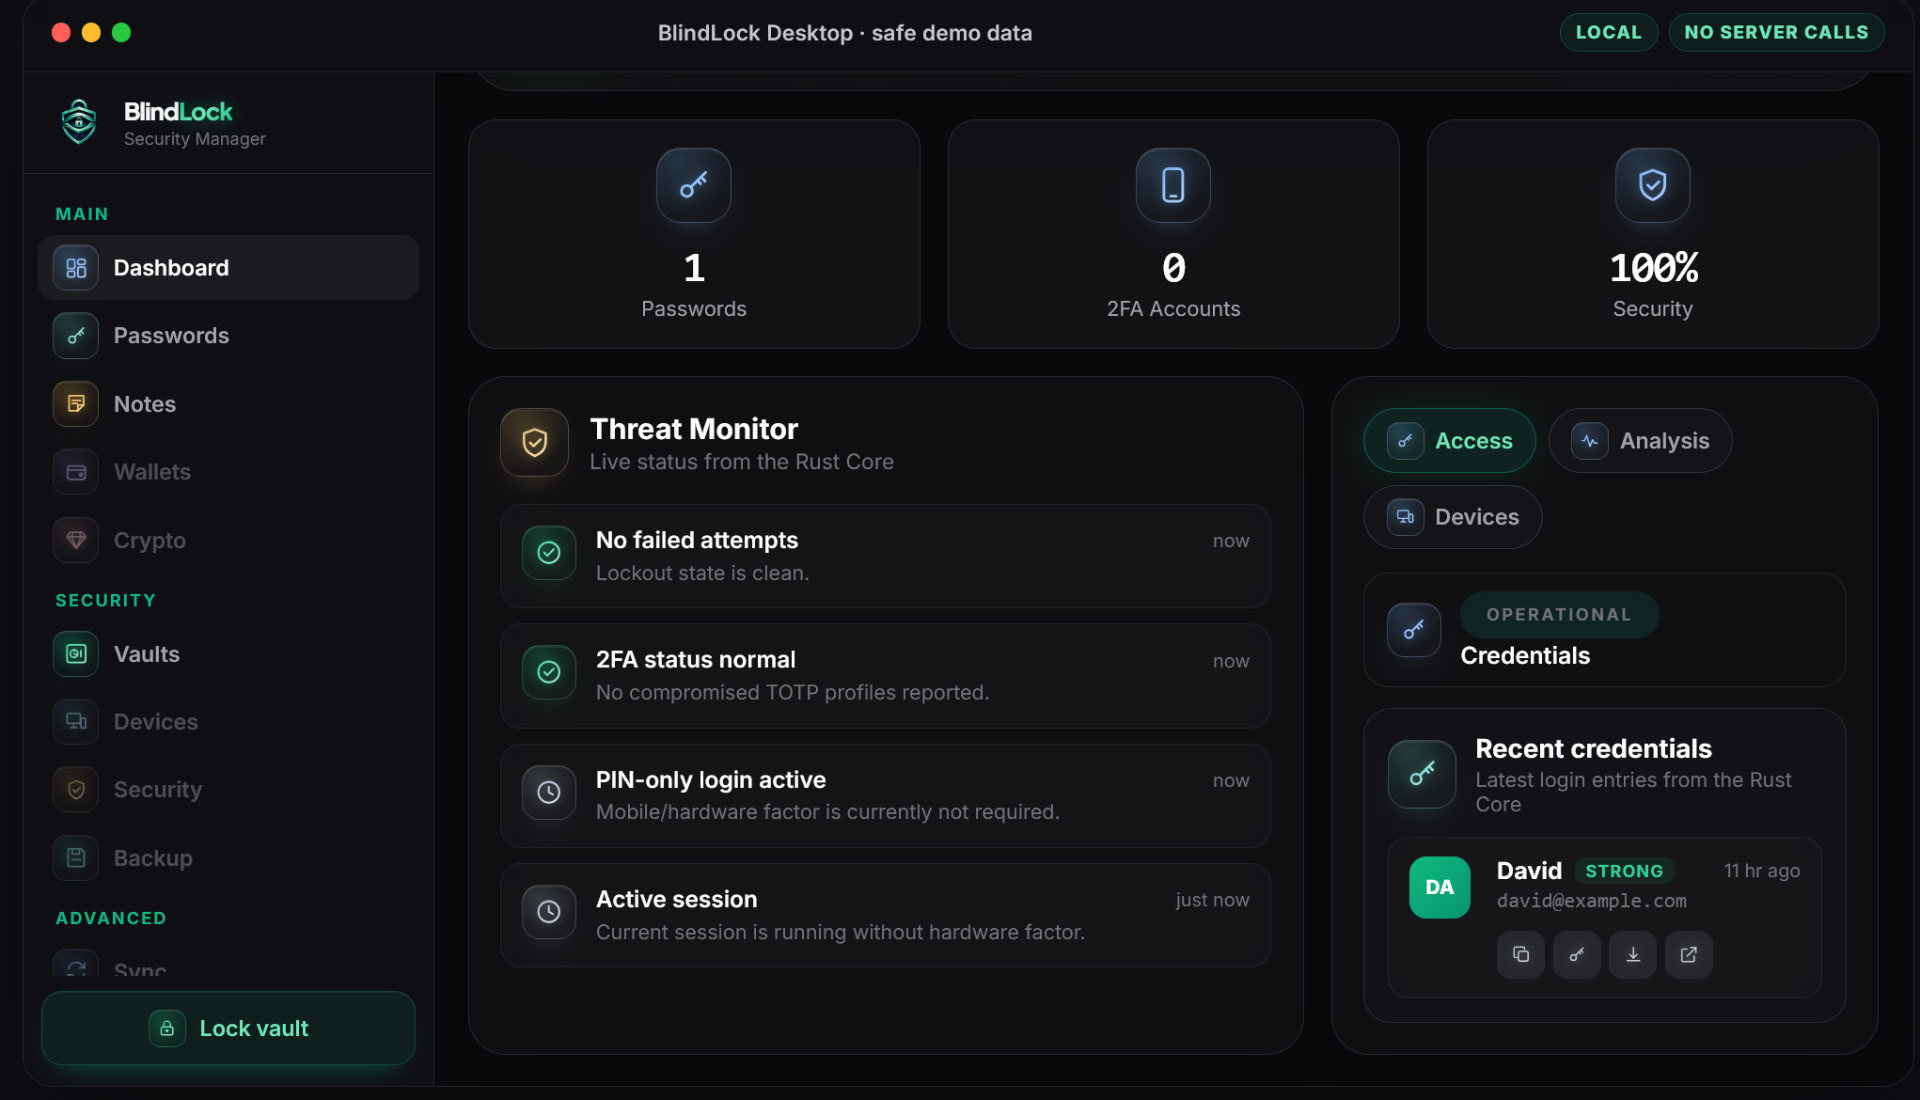
- BlindLock hides your password manager and secure vault in a PNG image — also offers secure notes, 2FA, and a crypto address book, with optional hardware security keys
BlindLock hides your password manager and secure vault in a PNG image — also offers secure notes, 2FA, and a crypto address book, with optional hardware security keys
A new local‑only password manager, notes app, and secure vault that hides your secrets in an ordinary-looking .PNG image file is now available. BlindLock does all this and more with an option to bind to your hardware using TPM2.0, Secure Enclave, or StrongBox. No cloud storage or central vault account is required, and the dev is selling lifetime licenses at $49 (for now). There is an interactive online demo, with nothing uploaded or downloaded, as well as a downloadable full 7-day demo available.
BlindLock’s solo developer David Domingo indicates that one of the main drivers behind his efforts to create this application was the theft of customer vault backups from LastPass in late 2022. What happened to LastPass could have also happened to 1Password, Dashlane, even Proton Pass, reckons Domingo. “When your vault sits on someone else's server, you inherit every risk that server carries: employee access, infrastructure vulnerabilities, government subpoenas, supply chain attacks, and the simple mathematical reality that a server holding tens of millions of vaults is a far more attractive target than your laptop,” says the BlindLock dev on his blog.
So, three independent layers of security apply to your BlindLock vault. It is invisible in its ordinary-looking PNG carrier, not just encrypted. BlindLock doesn’t run a central vault database, so there is nothing for attackers to steal from BlindLock servers and crack later. Your resting vault file uses 256-bit authenticated encryption and already includes NIST post-quantum components. It is also bound to your device. “The vault opens only when three things match: the carrier file, your master password and your authorized device,” asserts the BlindLock app page. “A copied file alone is not enough to gain access.”
BlindLock’s feature set is pretty broad for a new offering. Fully encrypted inside your chosen .PNG holiday snap or cat photo is a password manager, Markdown-supporting secure notes, a built-in 2FA authenticator, and an encrypted file vault (for any type of file), and there is support for an optional fourth-factor security key like a YubiKey or Google Titan, etc.
Accessing your BlindLock data requires three things at once: the carrier file, your master password, and the authorized device - the vault key is sealed to that device's security chip, which is TPM 2.0, Secure Enclave, or StrongBox depending on the platform. You can avoid overly bloating your central .PNG file by squirreling larger files separately in their own encrypted containers. BlindLock employs a hidden volumes system not unlike VeraCrypt for these containers. Domingo admits these are “not magically unfindable,” but are Argon2id-hardened, 256-bit authentication-encrypted and stored inconspicuously. For device loss or migration, users must create an encrypted BlindLock backup and keep its recovery phrase separately.
As per the intro, BlindLock is being introduced as a one-time $49 purchase. This perpetual pricing plan only applies to the first 1,000 licenses. There will be three waves: “the first 100 at $49, the next 350 at $89, and the final 550 at $109. After that, BlindLock is subscription-only,” says Domingo. The independent dev wants to lay a solid financial foundation, so development of BlindLock can continue.
This article is merely sharing the news about BlindLock and shouldn't be taken as a recommendation. Please check out the online and downloadable demos and judge whether it works for you and offers the features you want for the price.
OpenAI und über 100 Mitunterzeichner rufen zu stärkerer Cyberabwehr auf
Für Europa: Fraunhofer und SAP wollen US-Cloud-Anbieter austricksen
Der Beitrag Für Europa: Fraunhofer und SAP wollen US-Cloud-Anbieter austricksen erschien zuerst beim Online-Magazin BASIC thinking. Über unseren Newsletter UPDATE startest du jeden Morgen bestens informiert in den Tag.
![]()
Europäische Unternehmen hängen bei der digitalen Infrastruktur stark von US-Konzernen ab. Eine neue Open-Source-Architektur hinter Cloud Edge Computing soll nun die Wende einleiten und die Datenverarbeitung direkt vor Ort ermöglichen. Damit könnte eine unabhängige und nachhaltige digitale Infrastruktur in greifbare Nähe rücken.
Ein Blick auf die Internetinfrastruktur offenbart ein klares Bild: Wir in Europa zeigen eine deutliche Abhängigkeit von US-Konzernen, wie Amazon, Google oder Microsoft. Allein diese Anbieter verwalten etwa 70 Prozent der europäischen Infrastruktur. Im Resultat ist aber nicht immer ganz klar, wohin die Daten europäischer Bürger und Firmen fließen.
Eine Lösung des Problems könnten dezentrale Netzwerke sein. Derzeit entwickeln das Fraunhofer-Institut für Software- und Systemtechnik ISST und für Angewandte und Integrierte Sicherheit AISEC sowie SAP im Rahmen der EU-Initiative IPCEI-CIS eine Architektur (ApeiroRA), die zentrale Rechenzentren mit genau diesen dezentralen Netzwerken vereinen soll. Das könnte dann so aussehen, dass die Verarbeitung von Informationen innerhalb der Rechenzentren in sogenannten Cloud Edges erfolgt.
Was ist Cloud Edge Computing?
Bei Cloud Edges handelt es sich um dezentrale Rechenknoten, die Cloud-Dienste physisch näher an ihre Nutzer bringen. Denn das ermöglicht die Datenverarbeitung vor Ort und reduziert Latenzzeiten teils drastisch. In den Cloud Edges erfolgt die Analyse von Informationen in Echtzeit, während die Cloud weiterhin als zentraler Speicher dient.
Und hier besteht in Europa großes Potenzial. Denn solche Cloud Edges könnten etwa direkt im Turmfuß eines Windrads oder auf einem beliebigen lokalen industriellen Betriebshof entstehen. Heinrich Pettenpohl, Abteilungsleiter für IT Service Providers am Fraunhofer ISST, fasst zusammen:
Im globalen Markt für Public-Cloud-Dienste hat Europa den Anschluss verloren. Im Bereich von Cloud Edge Computing ist das nicht der Fall. Daher verfolgt die EU-Kommission die Strategie, dezentrale, kleinere Rechenzentren, sogenannte Cloud Edges, zu fördern, sodass europäische Unternehmen direkten Zugriff haben und ihre Daten dort ablegen können.
Das Projekt hat auch die Nachhaltigkeit im Blick. Denn digitale Arbeitslasten sollen laut Angaben dynamisch an diejenigen Standorte verlagert werden, an denen im jeweiligen Moment ausreichend Ökostrom zur Verfügung steht.
Offene Standards für europäische Unternehmen
Für Unternehmen und Behörden bringen die offenen Schnittstellen weitere Vorteile. In sich isolierte Insellösungen sollen dann nämlich der Vergangenheit angehören. Denn der neue Ansatz soll erstmals eine besonders hohe Flexibilität und Interoperabilität bieten. Eine strikte Bindung an nur einen Anbieter findet dann nicht mehr statt.
Die Fraunhofer-Institute beschreiben auch konkrete Zukunftsszenarien. Intelligente Systeme könnten etwa zur Optimierung des eigenen Ressourcenverbrauchs digitale Zwillinge simulieren. Durch die Auswahl der besten Simulation ließe sich im Resultat dann die optimale IT-Konfiguration finden. Eine autonome Fehleranalyse und KI-gestützte Betriebsführung sollen Administrationsaufwände deutlich reduzieren.
Für die unabhängige Weiterentwicklung übergaben die Projektpartner ihre zentralen Ergebnisse an die NeoNephos Foundation. Diese ist Teil der Linux Foundation Europe und soll bald die komplexe Architektur schrittweise in konkrete Lösungen und Piloten überführen. Dabei sind höchste Sicherheitsstandards unverzichtbar, um die Informationen vor unbefugten Zugriffen zu schützen. Im besten Fall entsteht also eine übertragbare Lösung, die Europa mehr Unabhängigkeit, Transparenz und eine langfristige Wettbewerbsfähigkeit ermöglicht.
Auch interessant:
- ChatGPT hat jetzt einen Lockdown-Modus – so kannst du ihn aktivieren
- Privat mit KI chatten: Inkognito-Chat mit Meta AI in WhatsApp starten
- Elektroauto in der Sommerhitze: 5 Tipps, um deinen Akku zu schonen
- E-Auto-Förderung 2026 mit bis zu 6.000 Euro – so bereitest du den Antrag vor
Der Beitrag Für Europa: Fraunhofer und SAP wollen US-Cloud-Anbieter austricksen erschien zuerst auf BASIC thinking. Folge uns auch auf Google News und Flipboard oder abonniere unseren Newsletter UPDATE.